Technologies, with versions
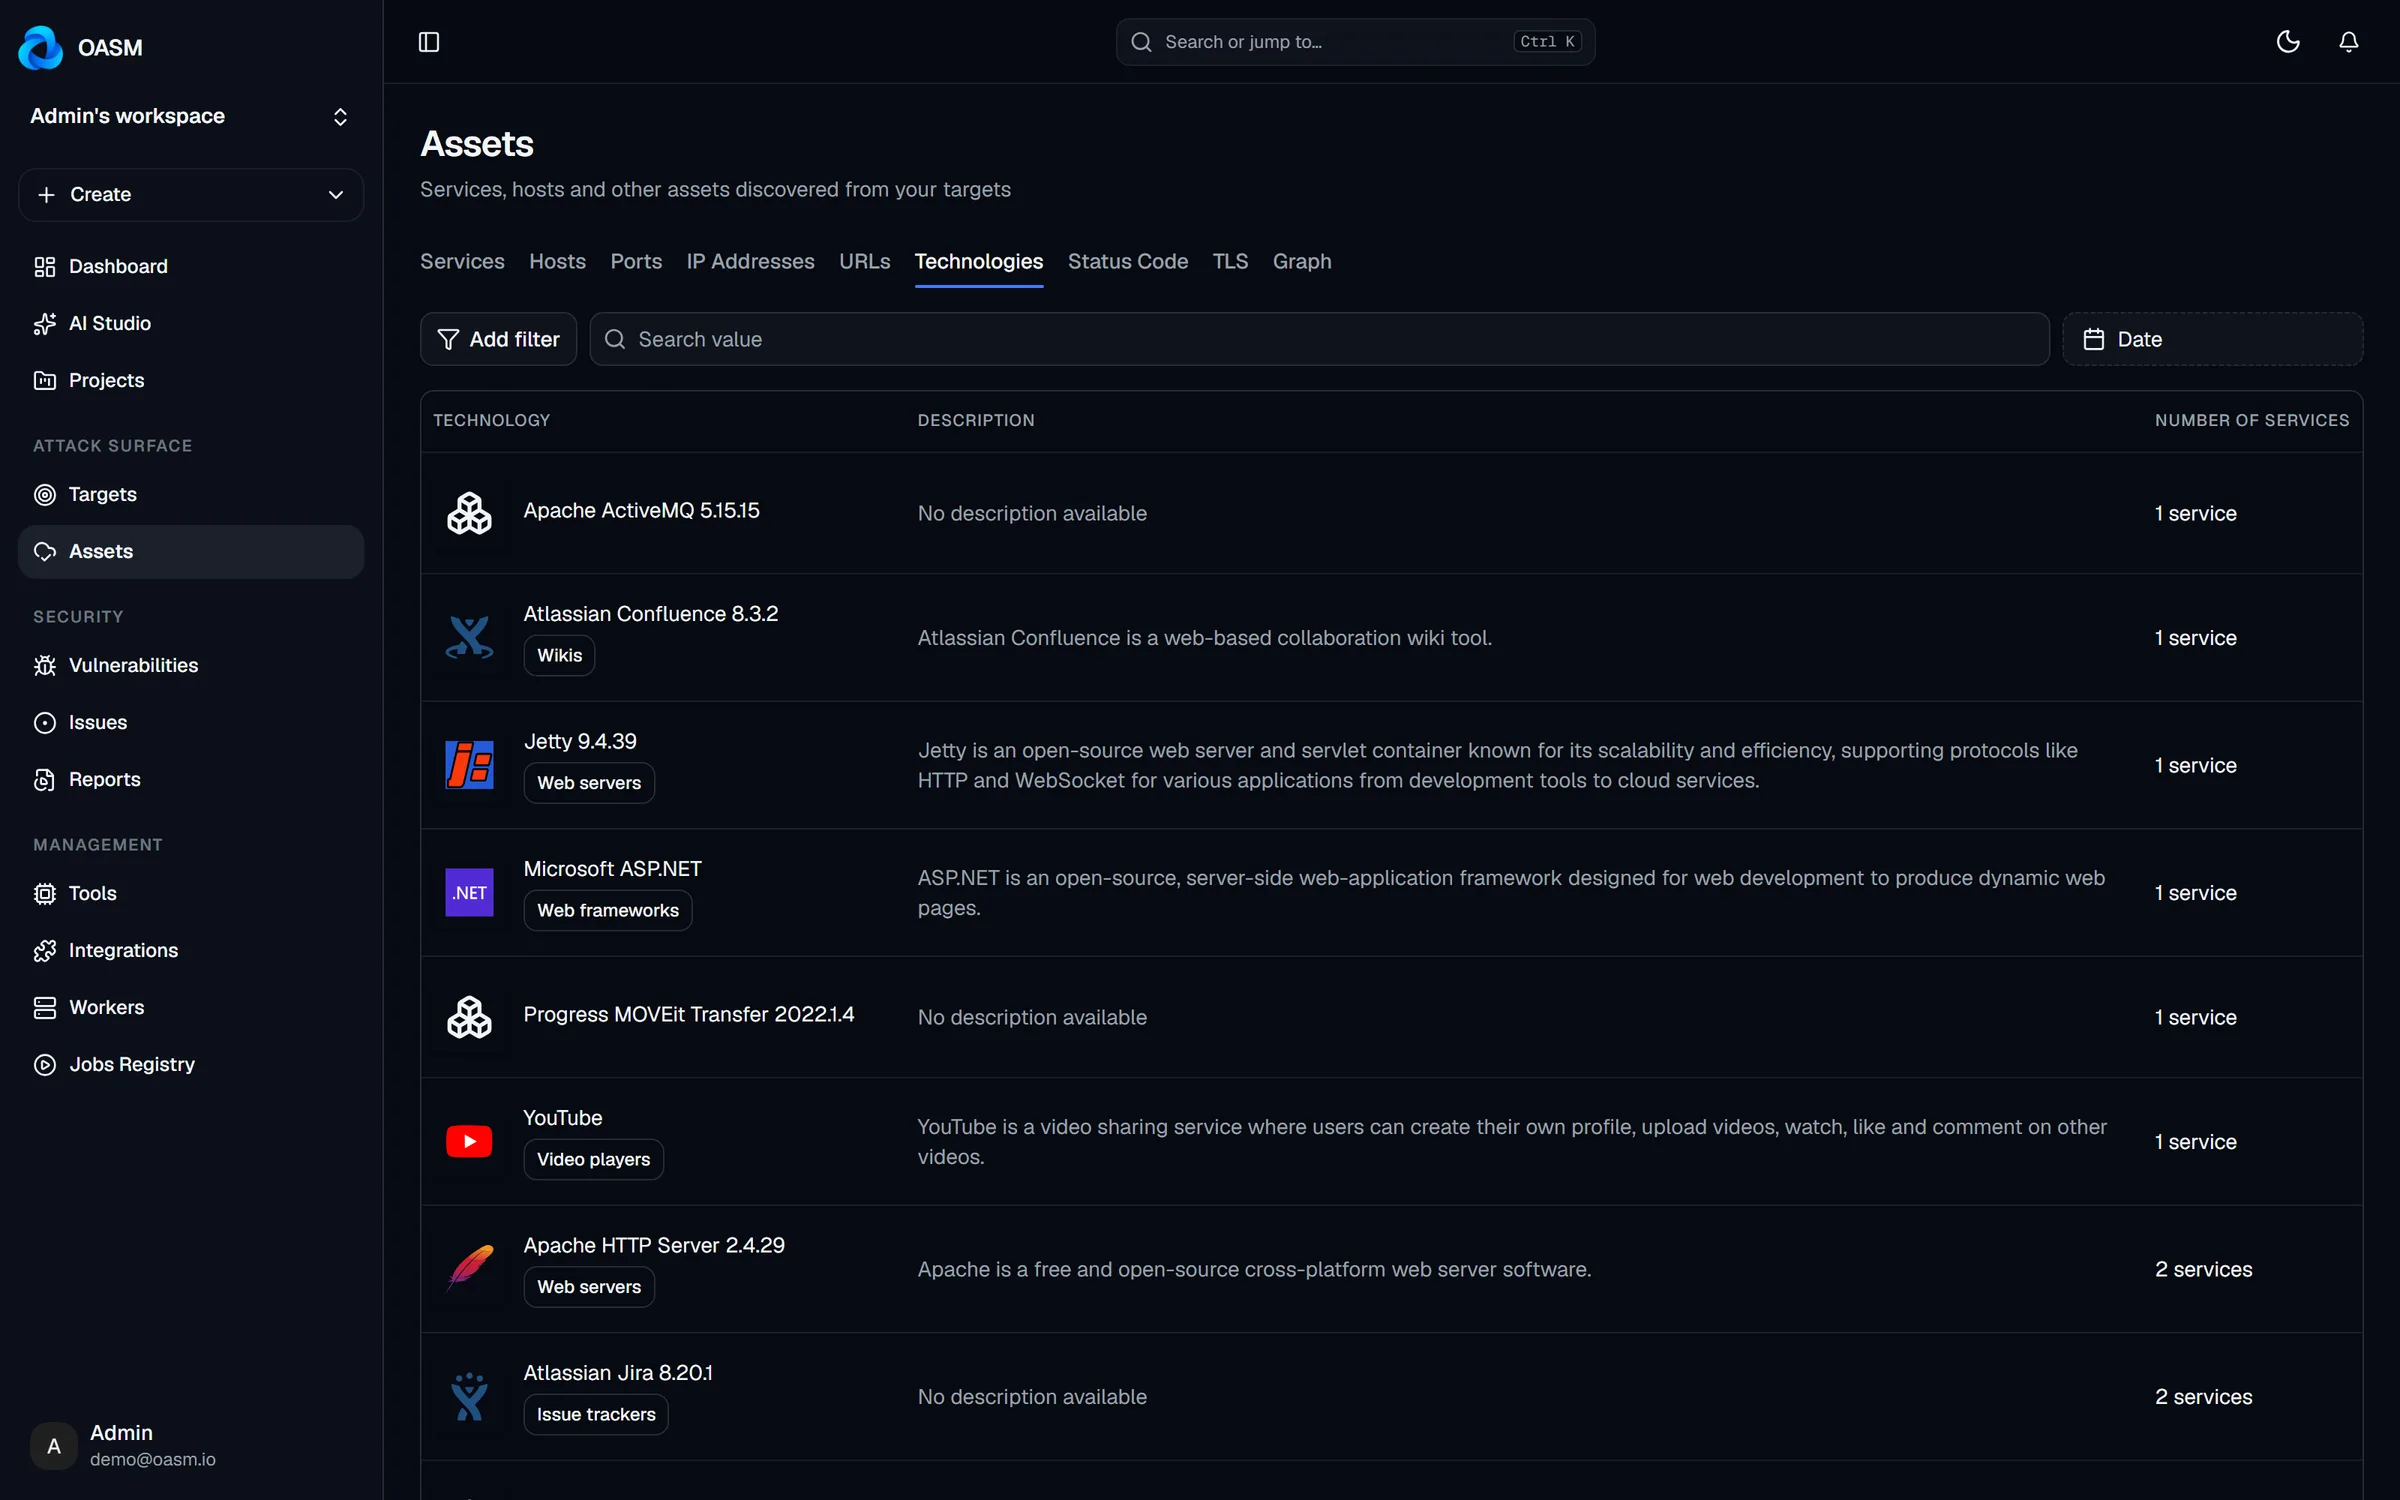
Spot every host running an outdated Confluence, MOVEit or ActiveMQ build.
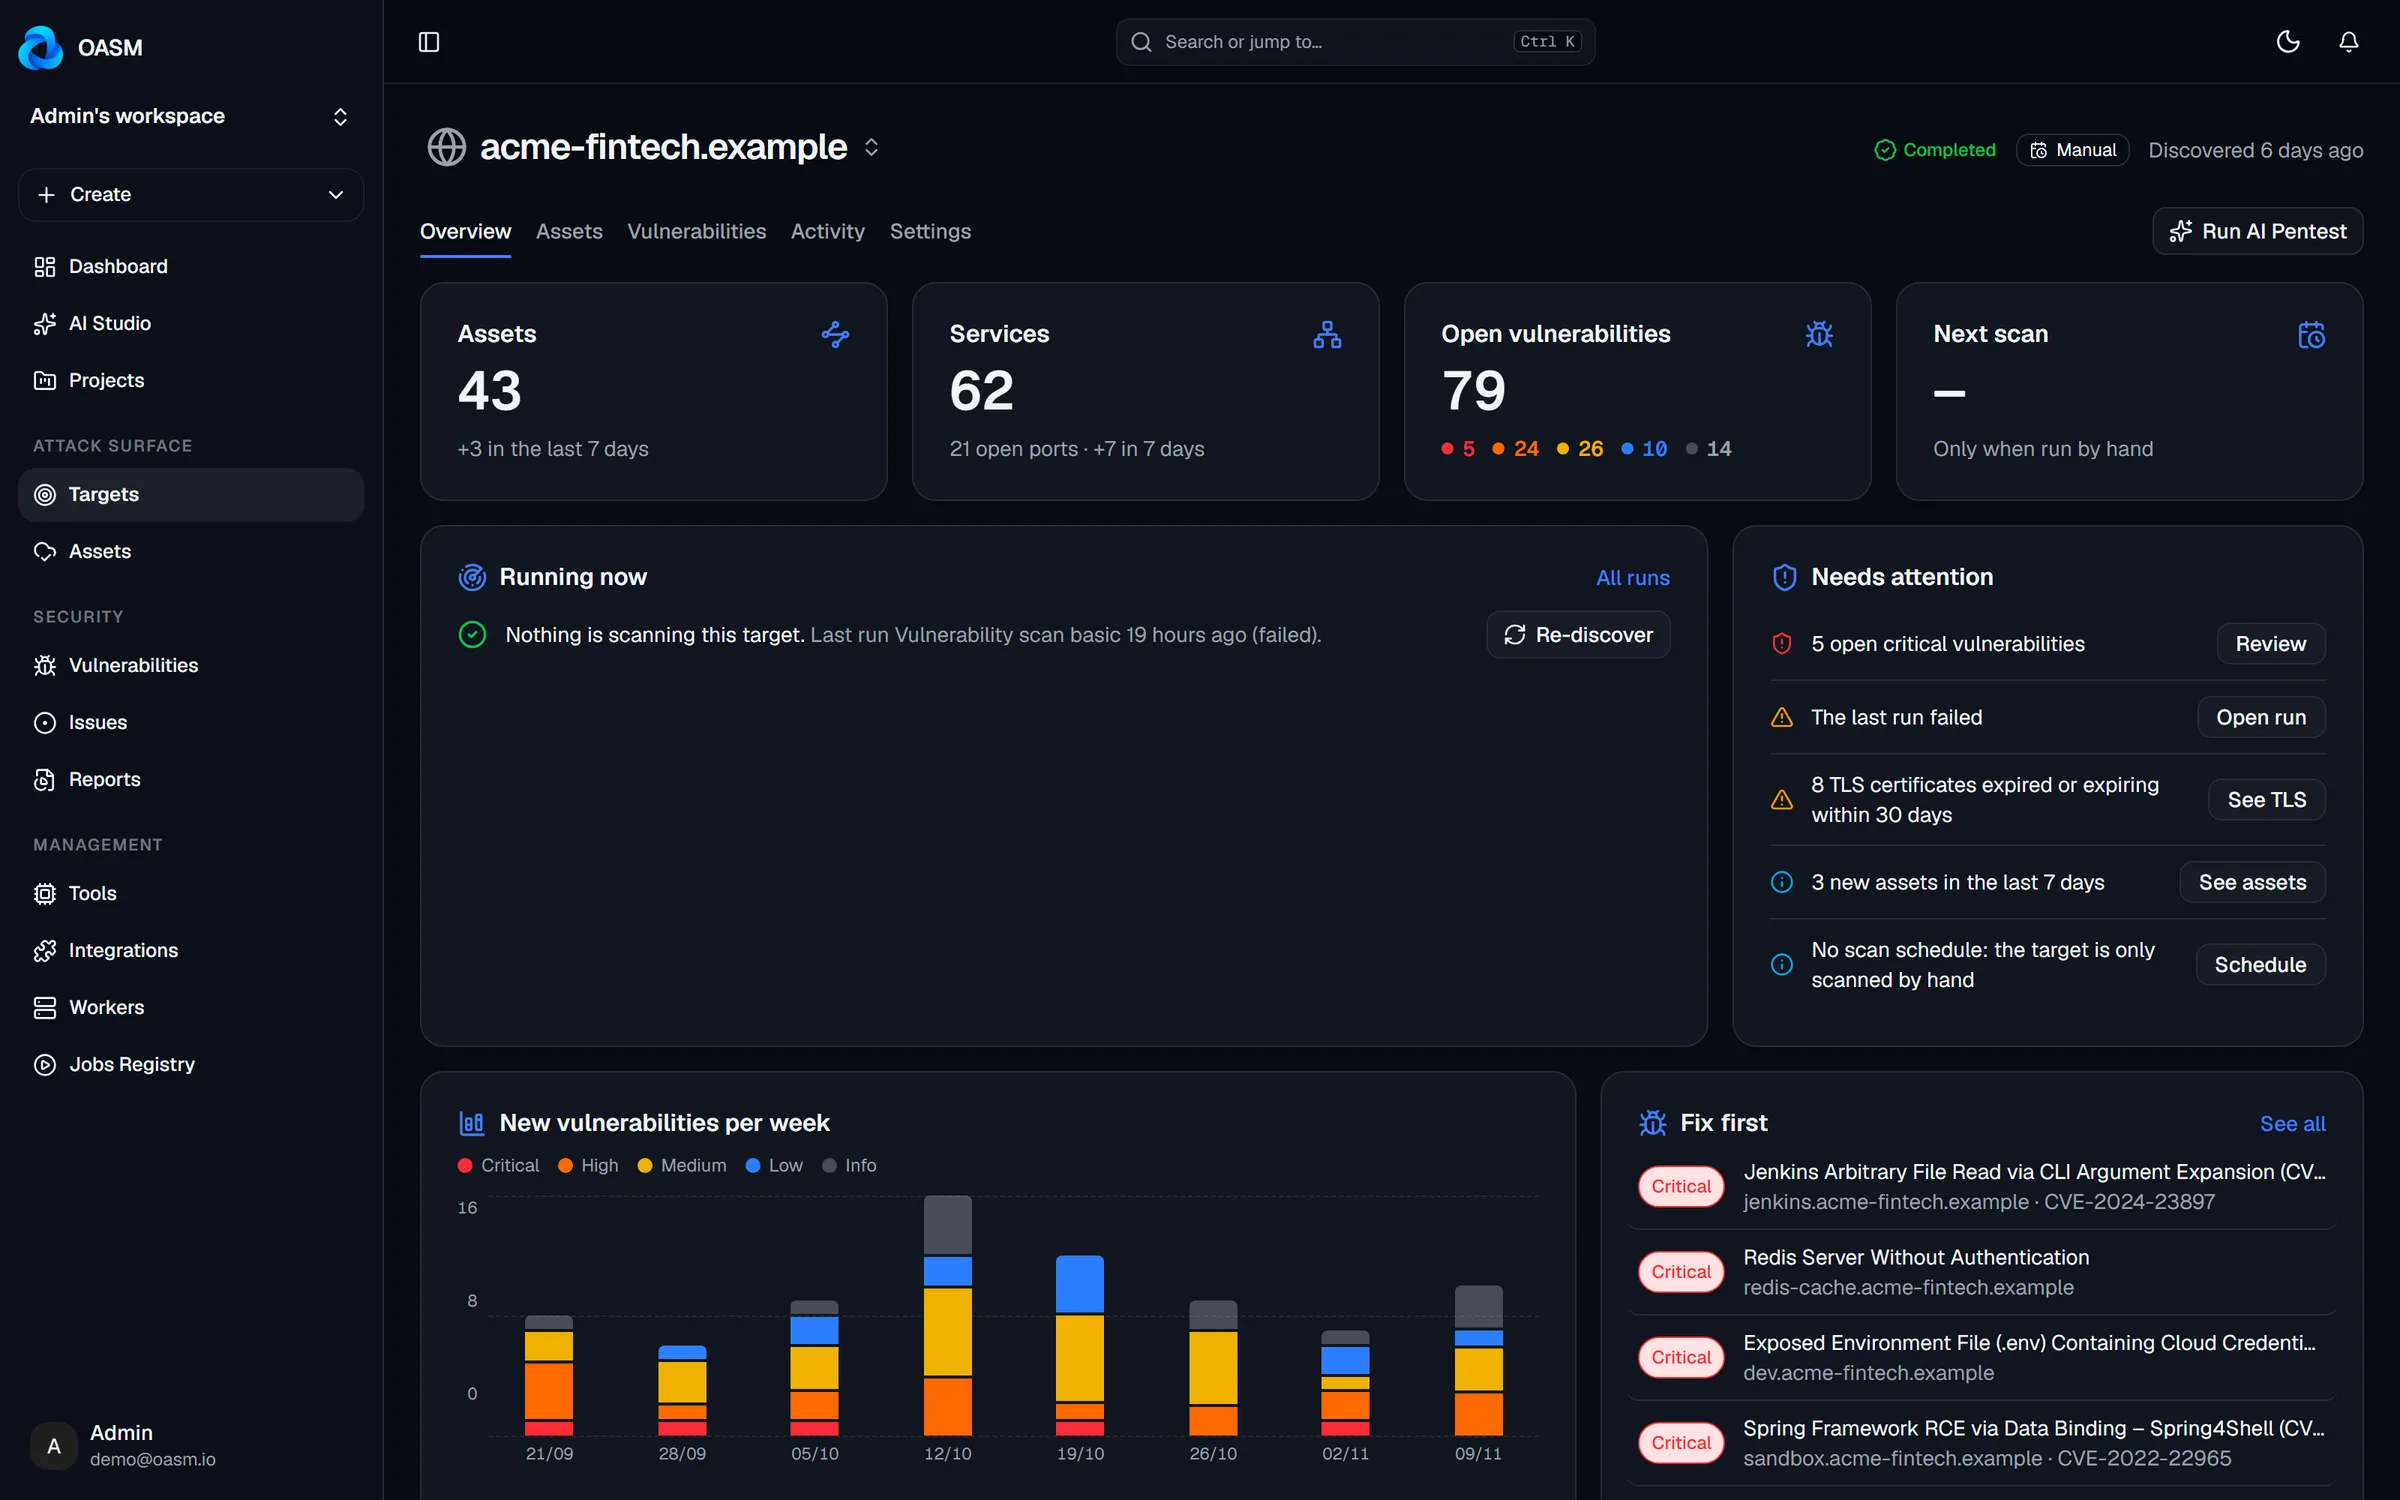
Every host, port, service, technology and TLS certificate — deduplicated, enriched and tracked over time, so you always know what is out there.
✓ Hosts, ports, URLs and IPs✓ Technologies with versions✓ Expiring certificates flagged
THE PROBLEM
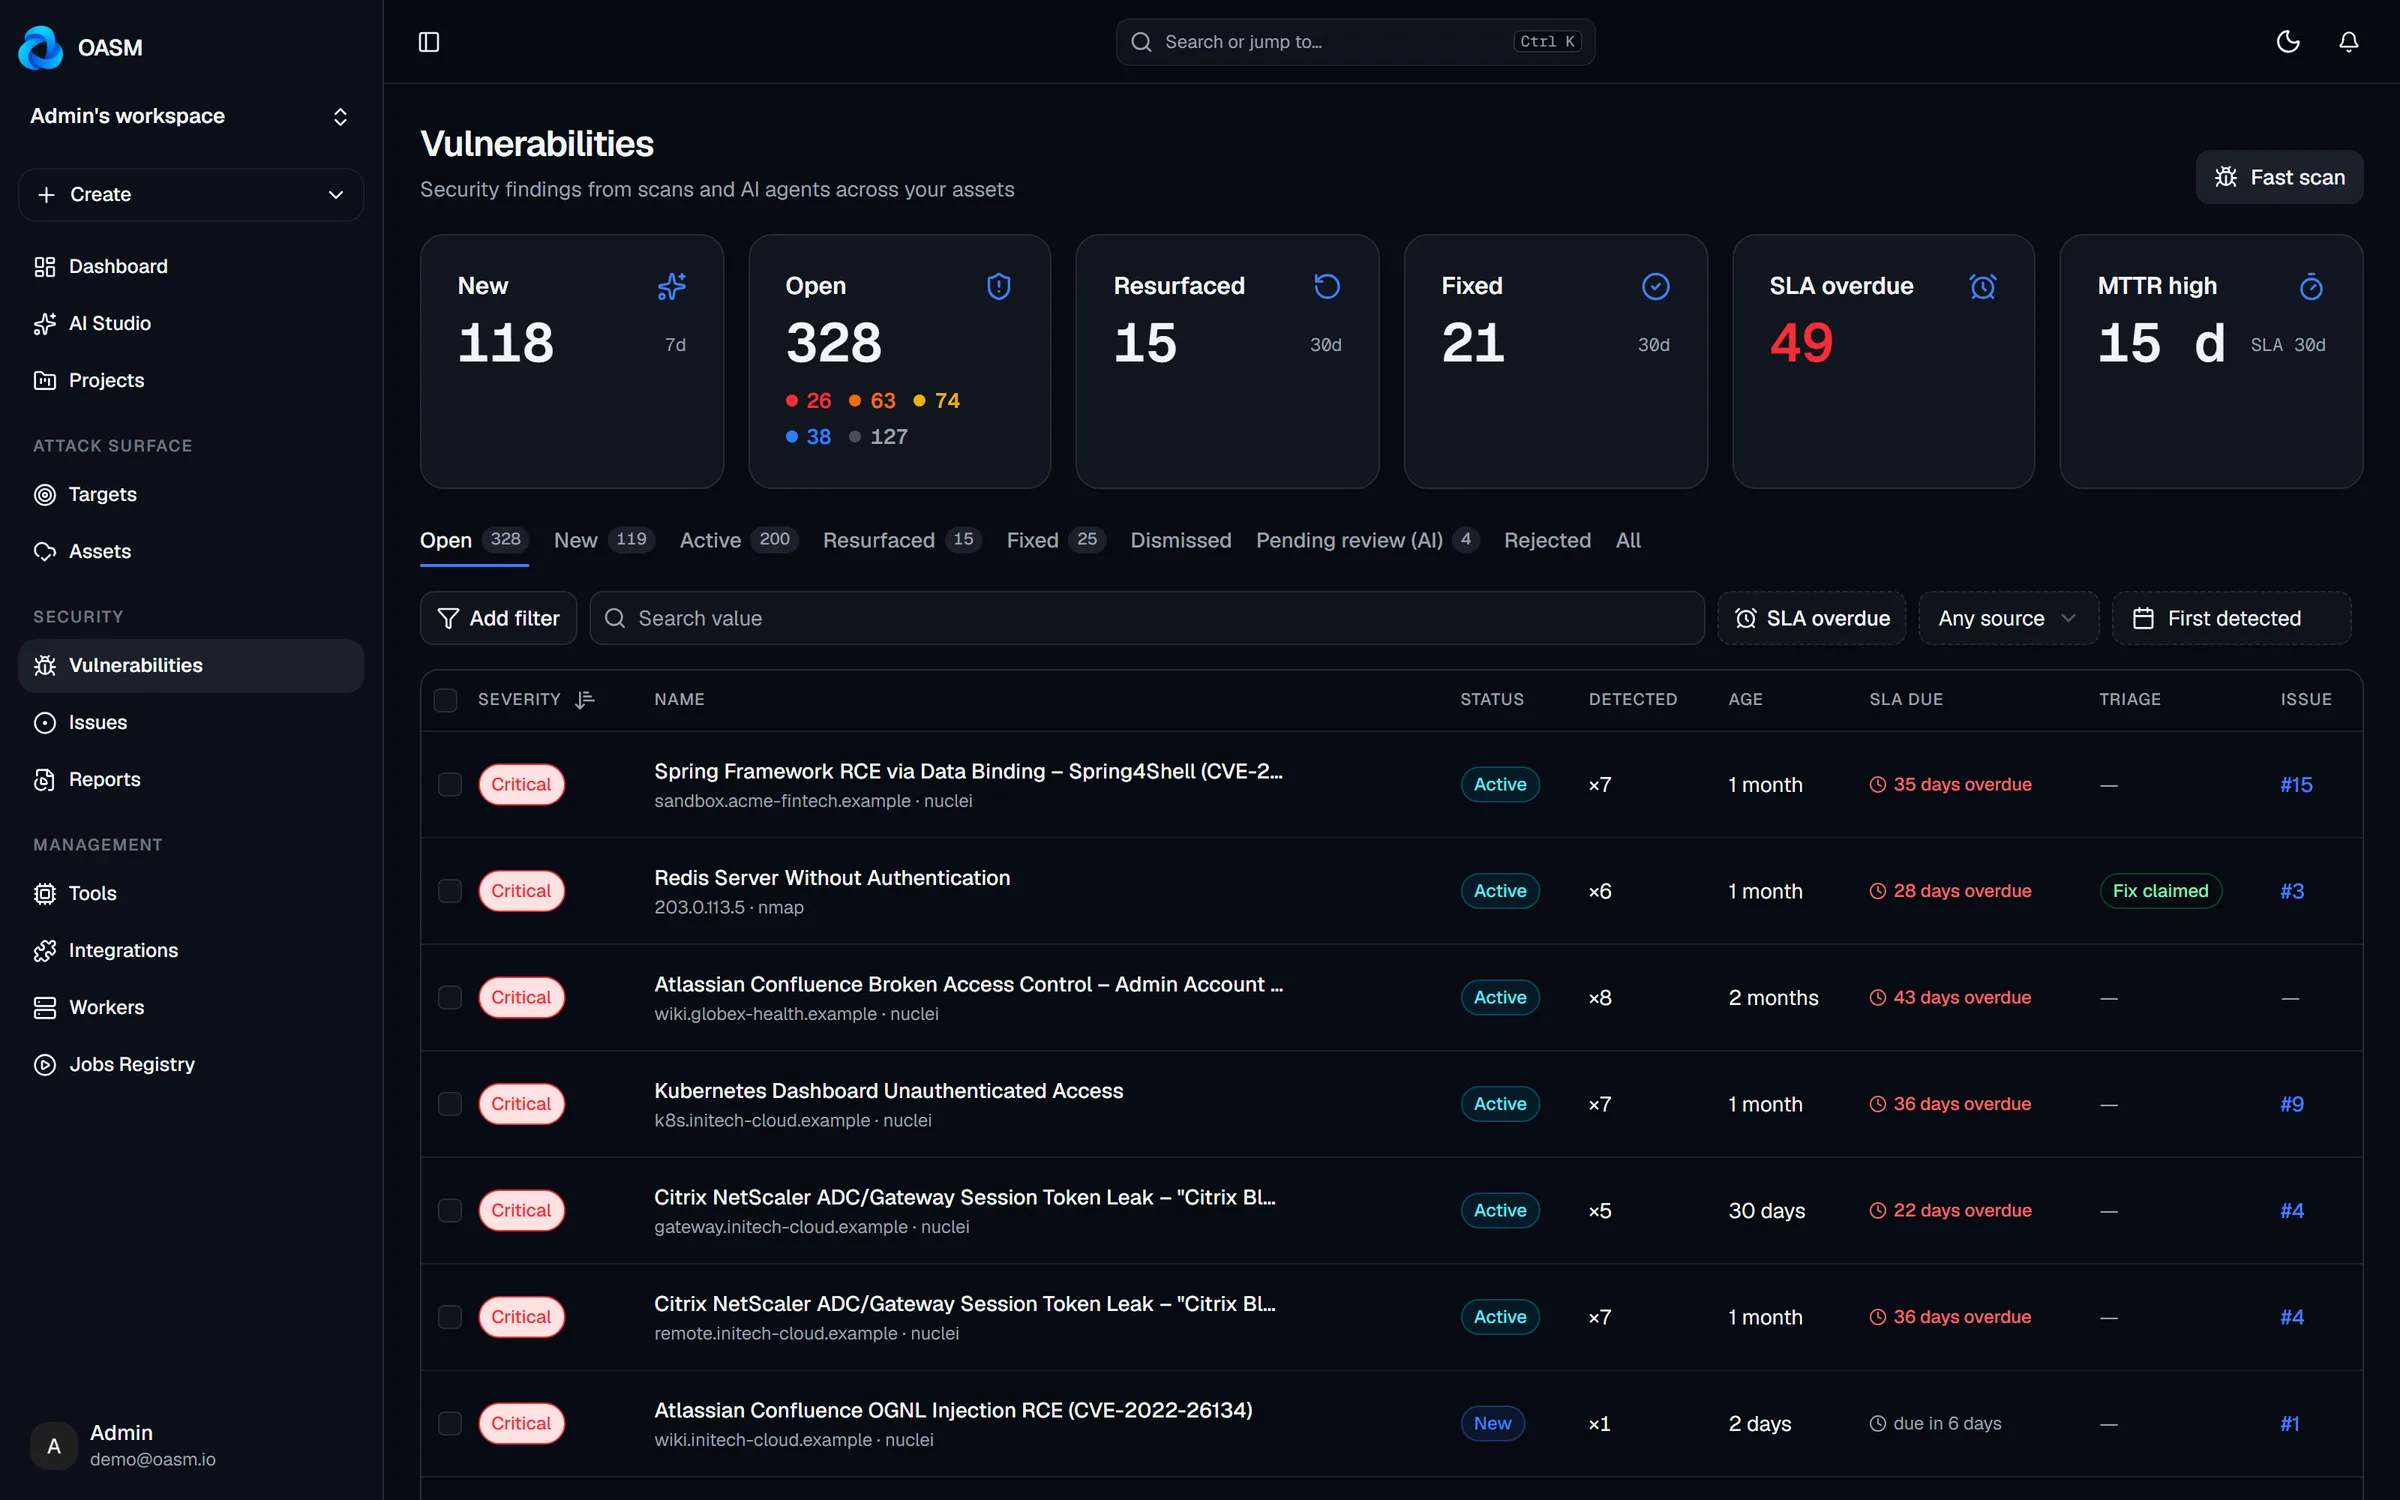
A new CVE lands at 9am. Can you say by 9:05 which of your hosts run the affected version? With OASM, it is one filter away.
Every scan adds and updates hosts, ports, services and technologies.
HTTP responses, certificates, IP data and screenshots attach to each asset.
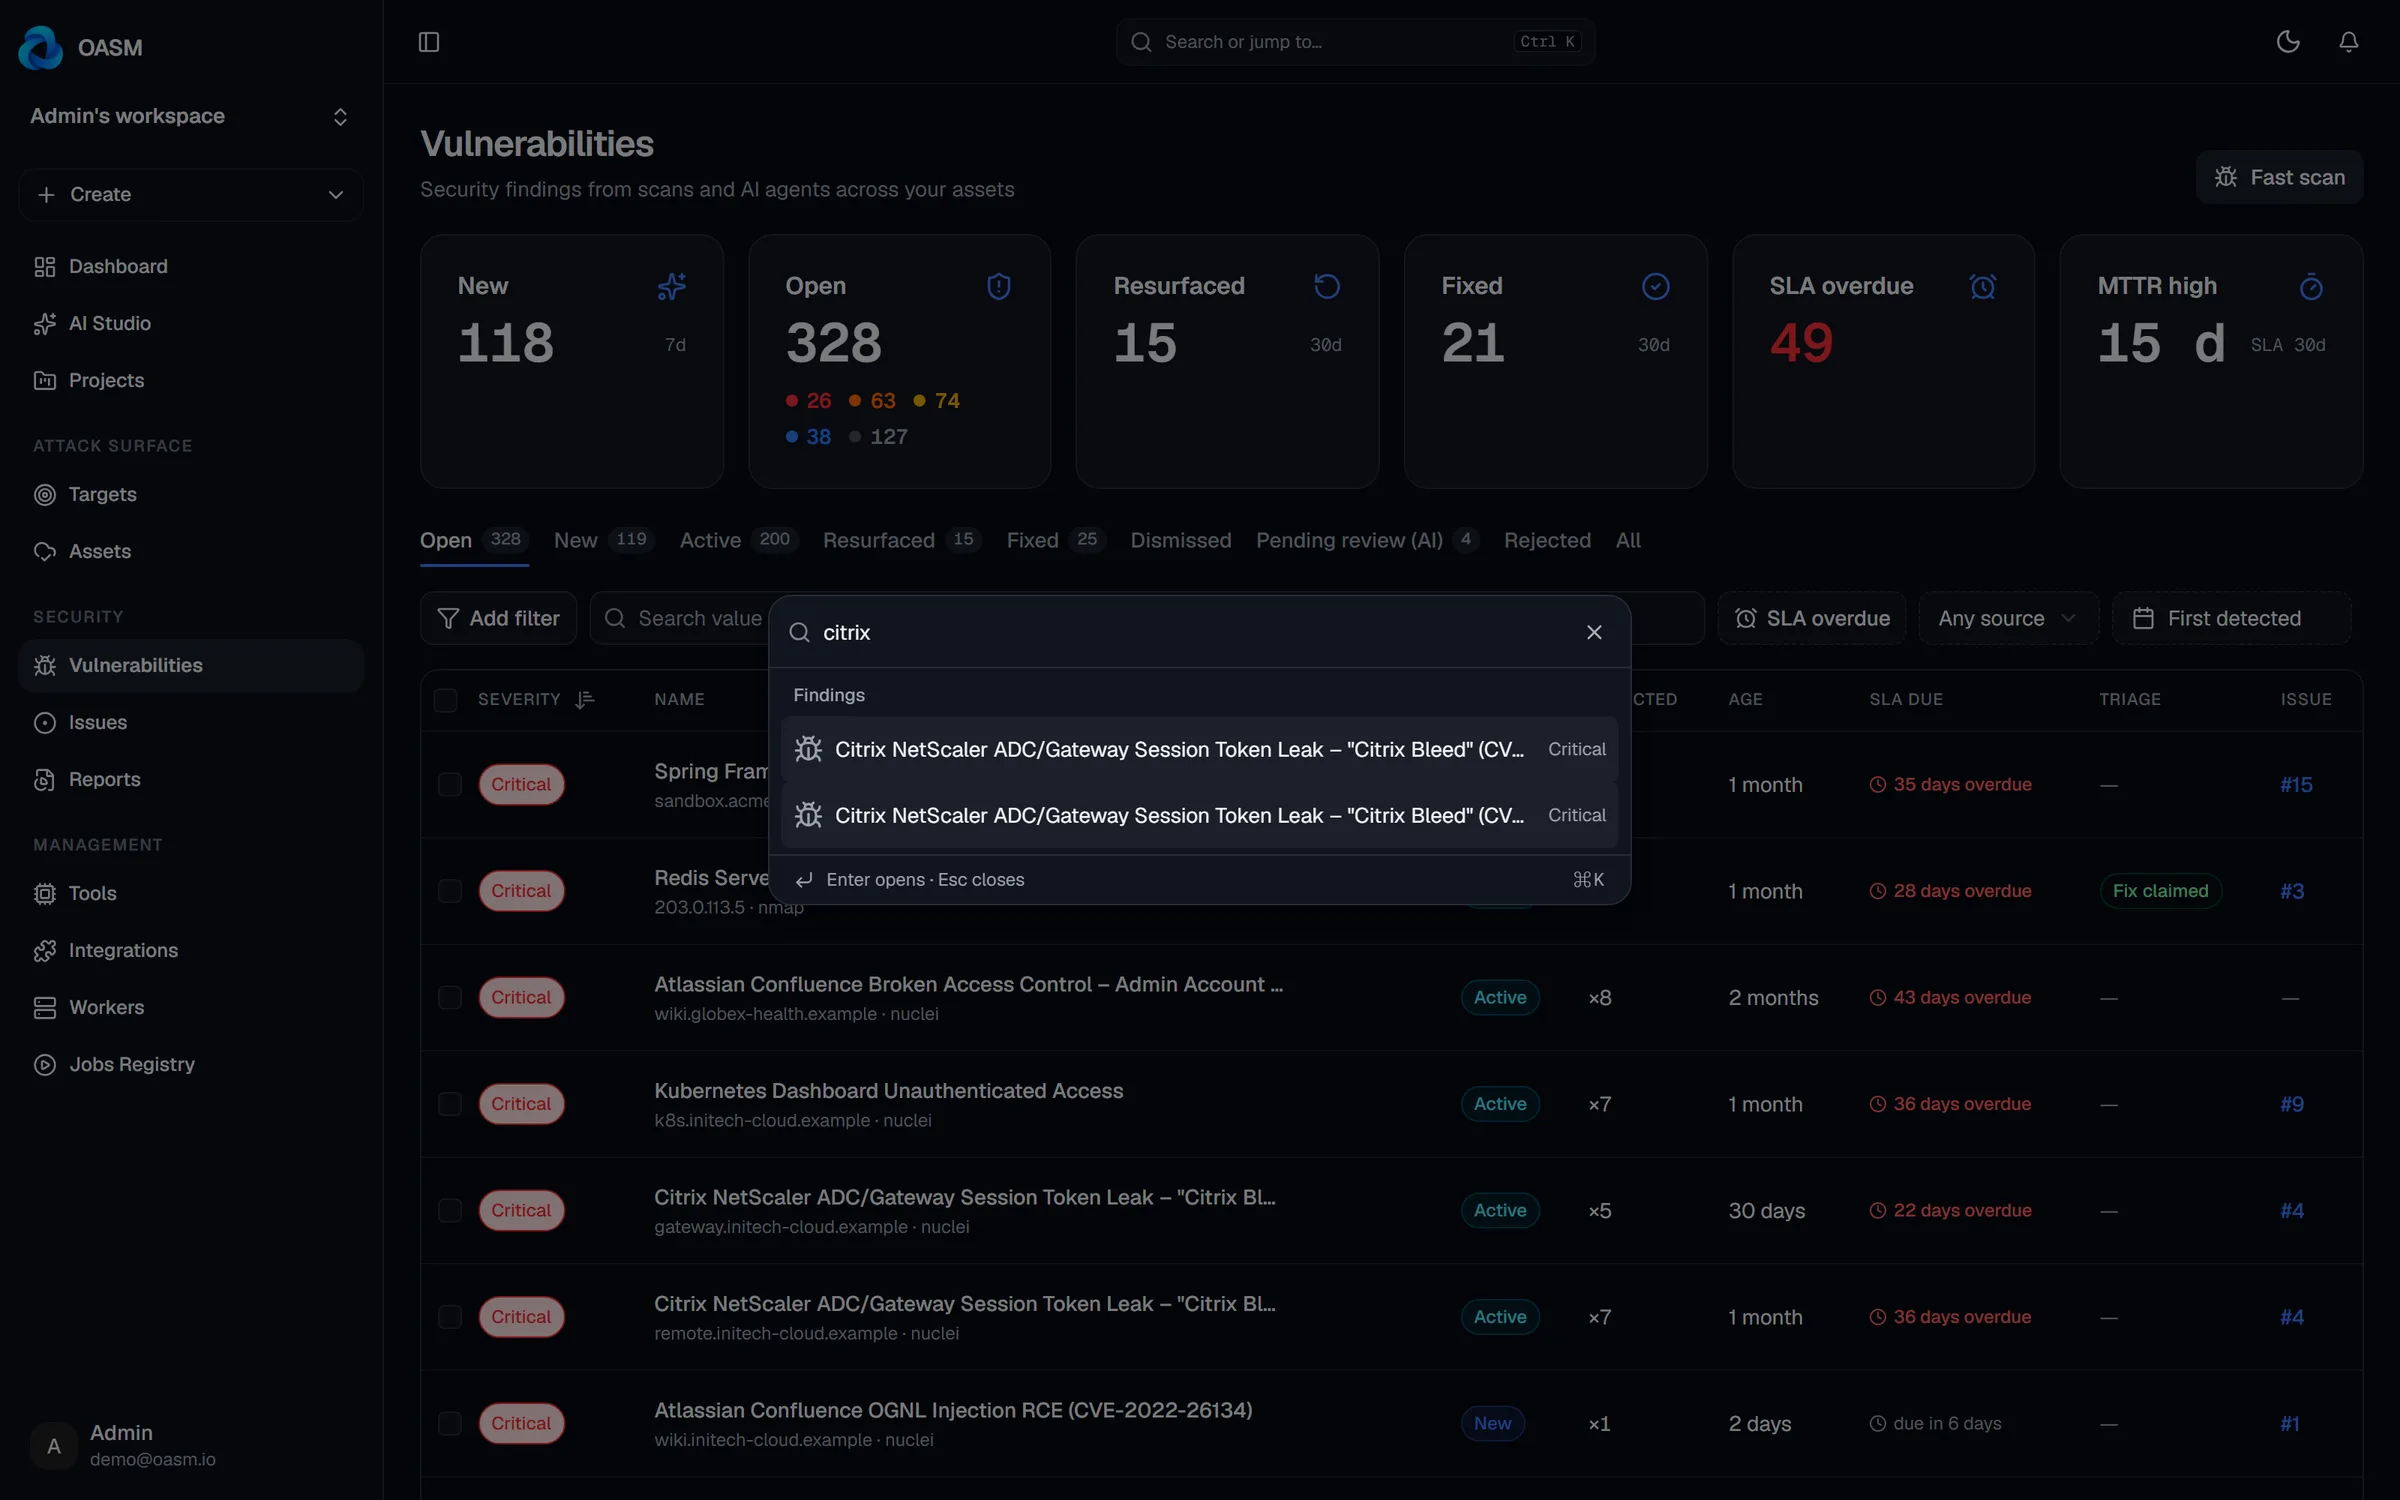
Filter, pivot and export any view — or ask AI Studio about it.
Switch views to see the same surface by technology, certificate, port or status code.
Spot every host running an outdated Confluence, MOVEit or ActiveMQ build.
Expired and soon-to-expire certificates surface on their own.
How many services sit behind each exposed port.
Crawled endpoints and their HTTP status.
See how domains, IPs and services connect.
Slice by any field and export the result.
Every certificate with its subject, protocol and expiry date — overdue ones in red.
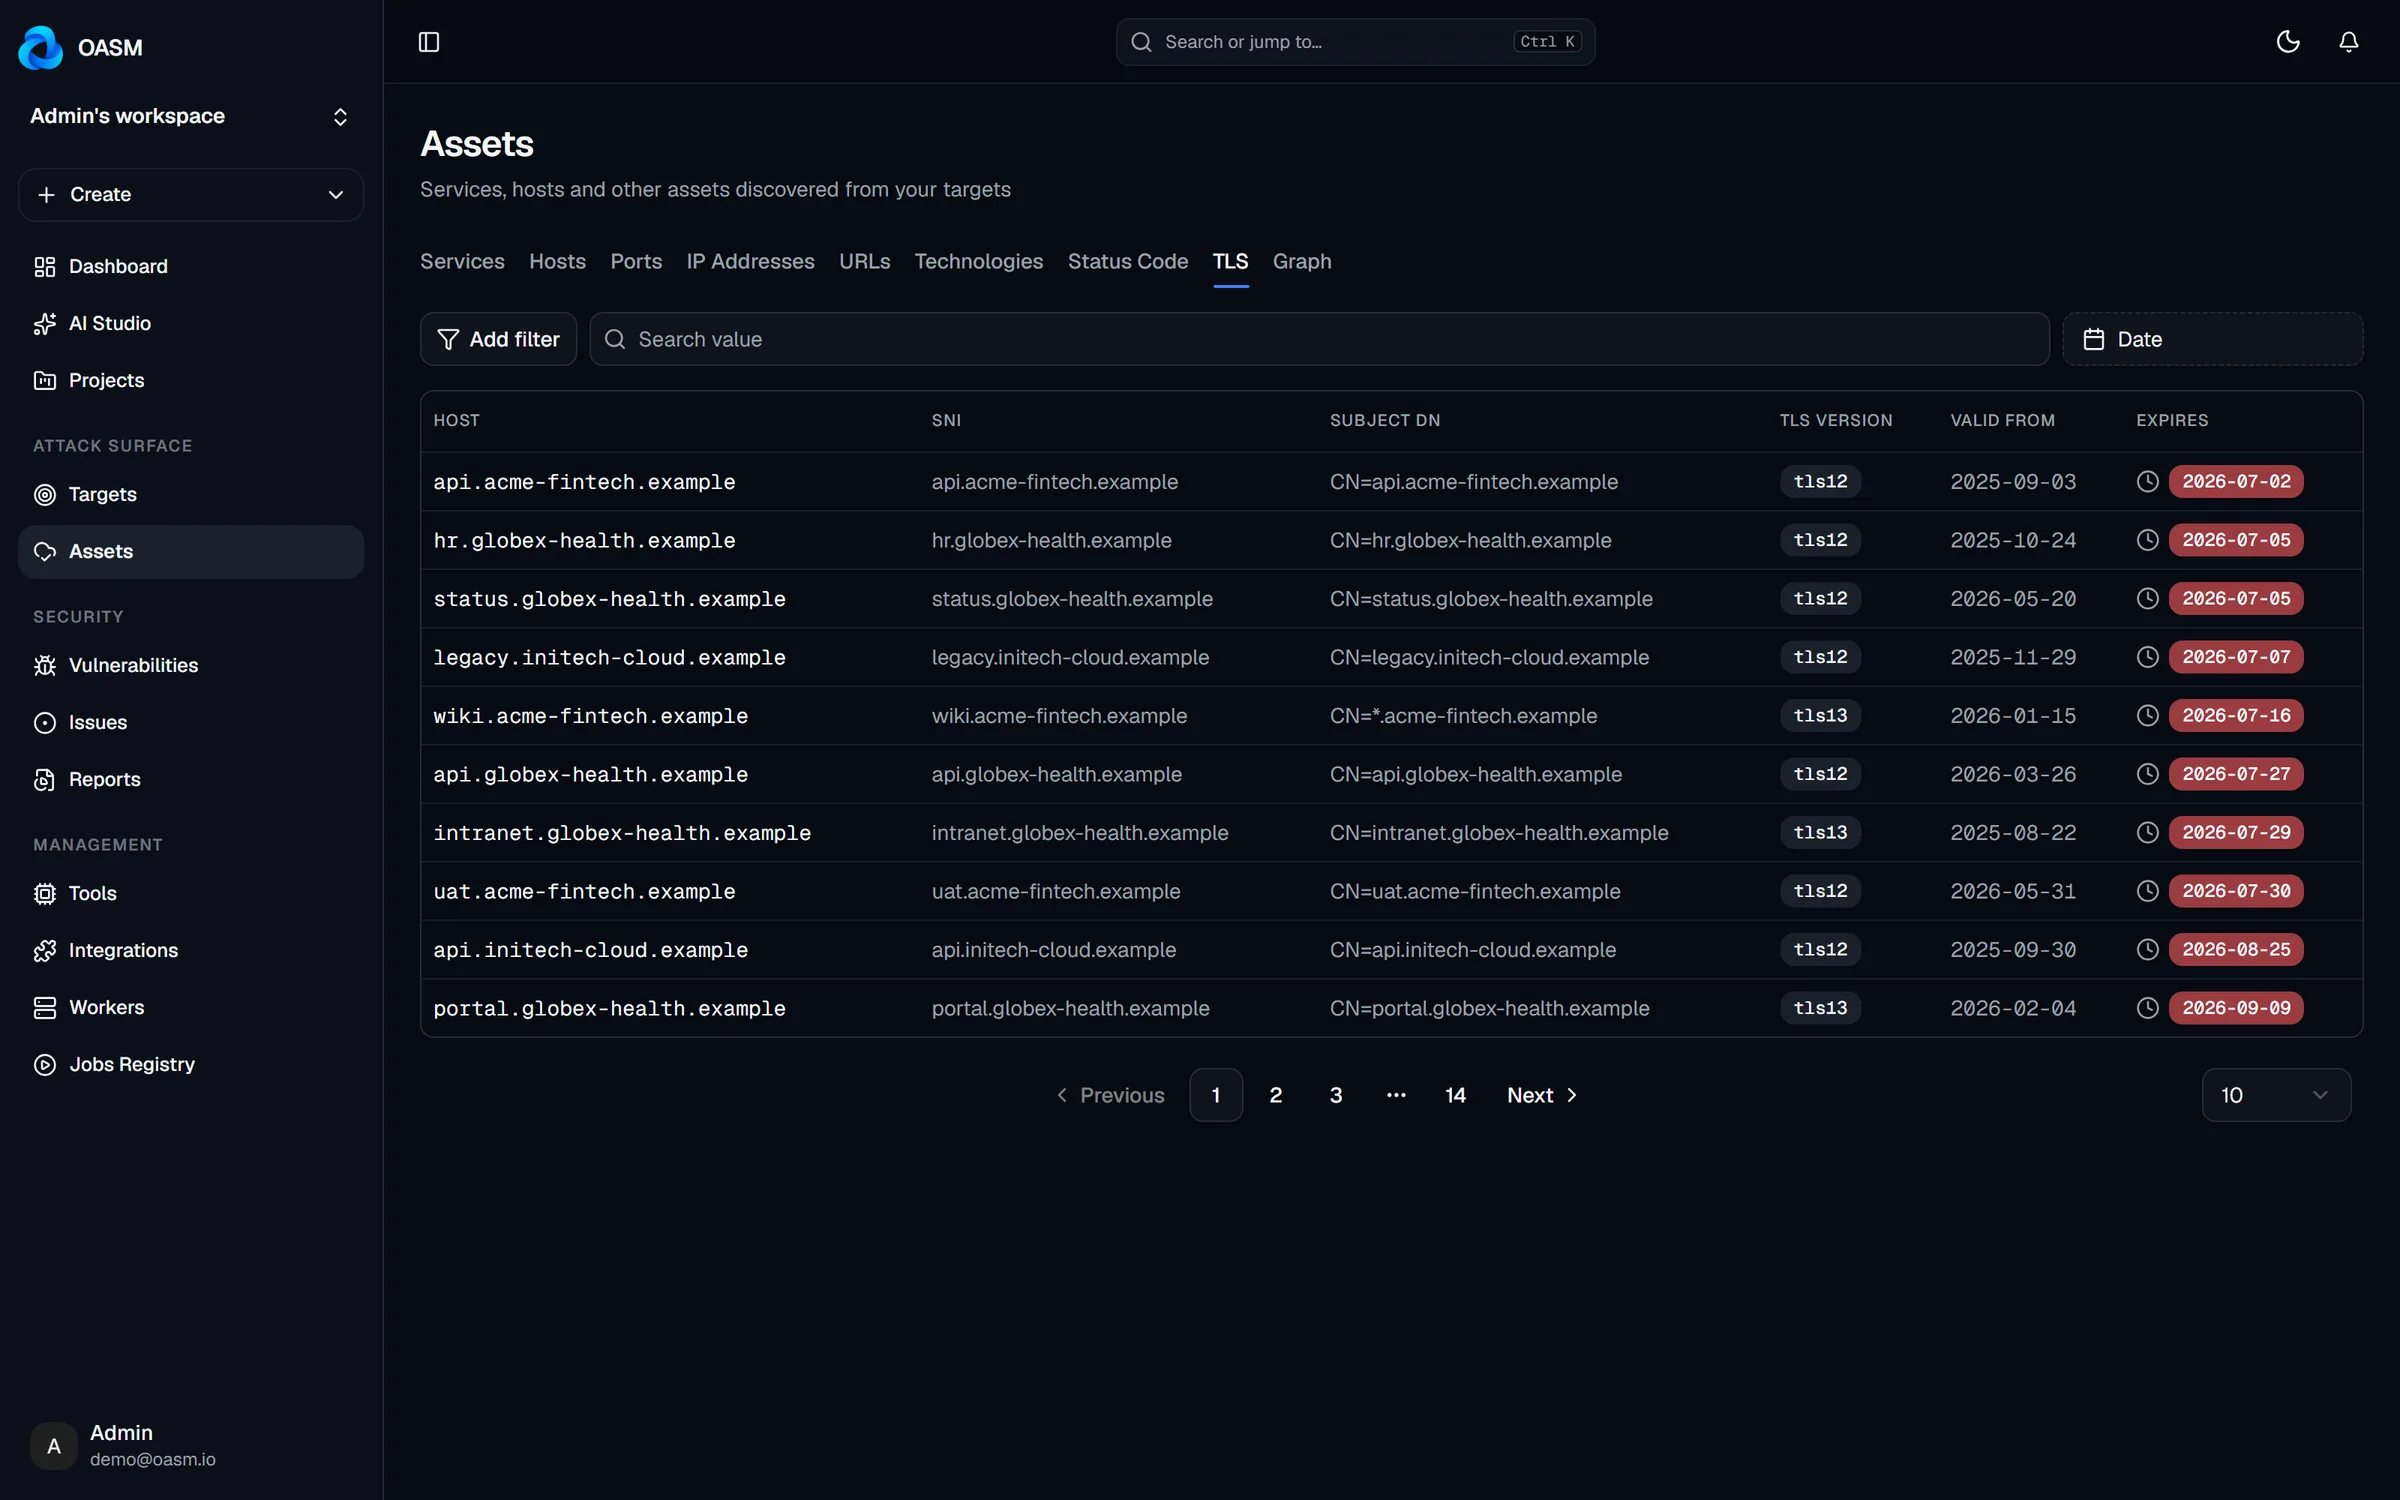
See which ports are exposed across the surface and how many services answer on each.
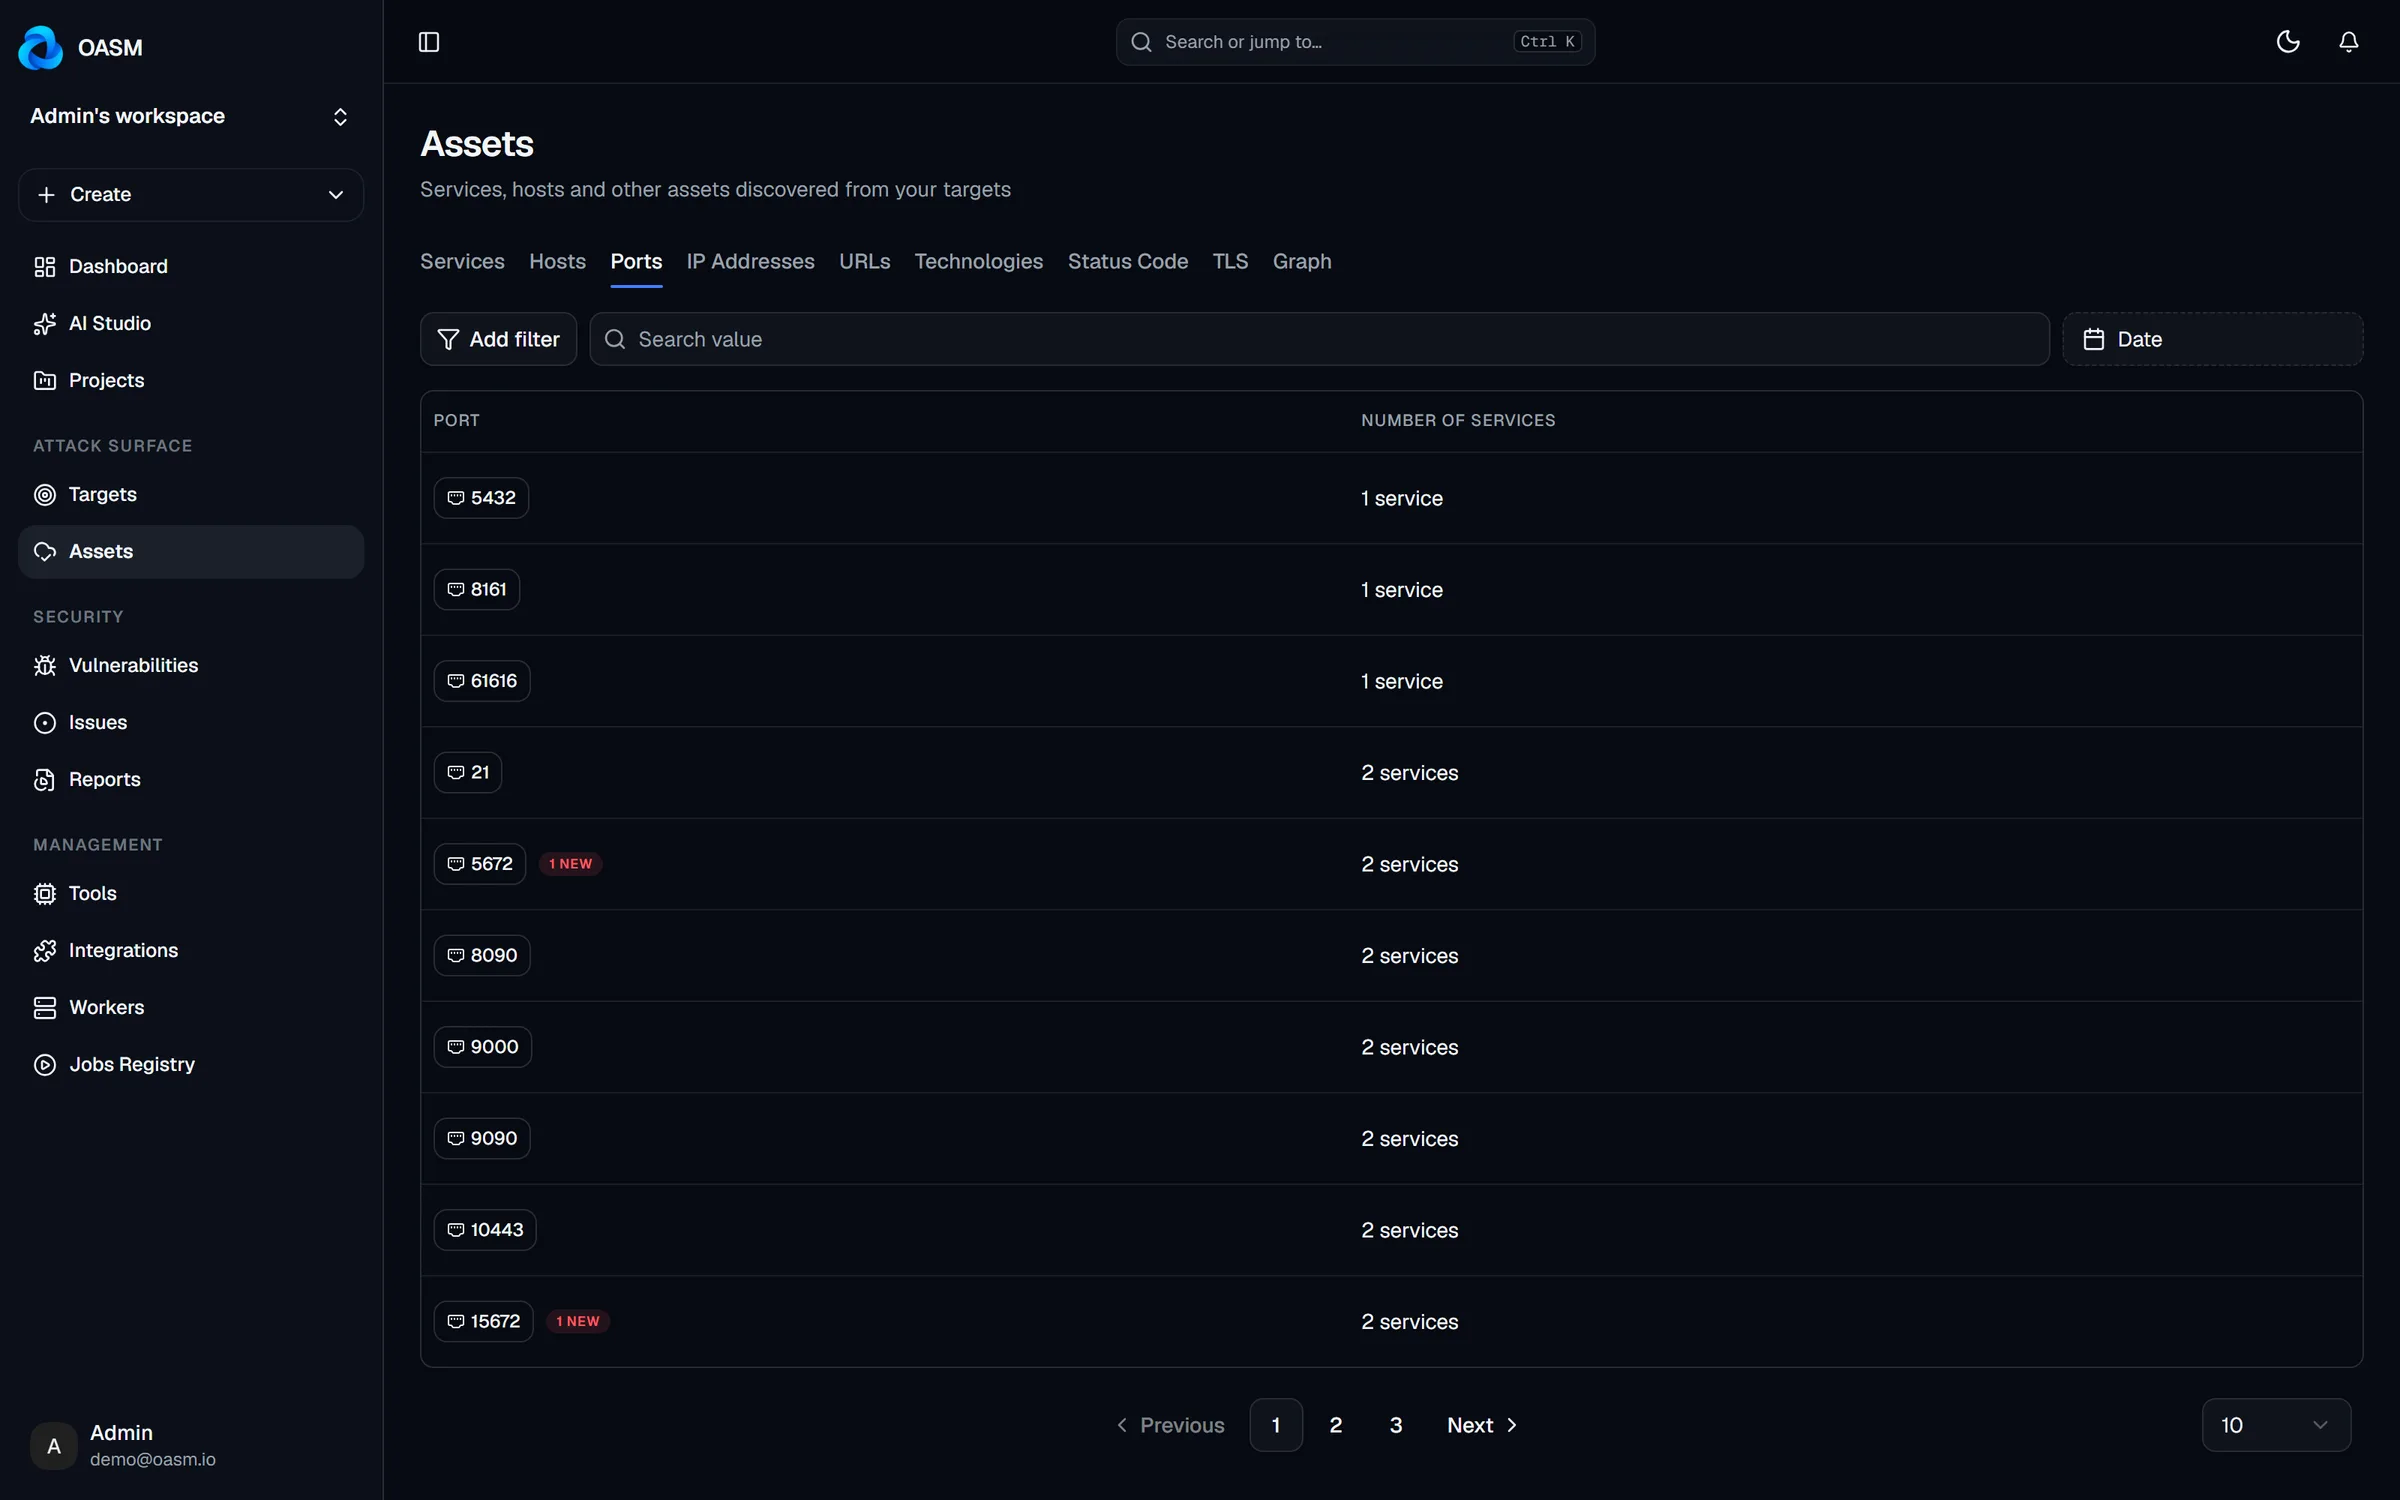
Find every host running a vulnerable version the moment a CVE drops.
Catch certificates before they expire and break customer traffic.
Export a current inventory for any audit or questionnaire.
From discovery scans, scanner connectors and cloud or repository integrations — all deduplicated per workspace.
Free, open source and self-hosted. Your data never leaves your infrastructure.