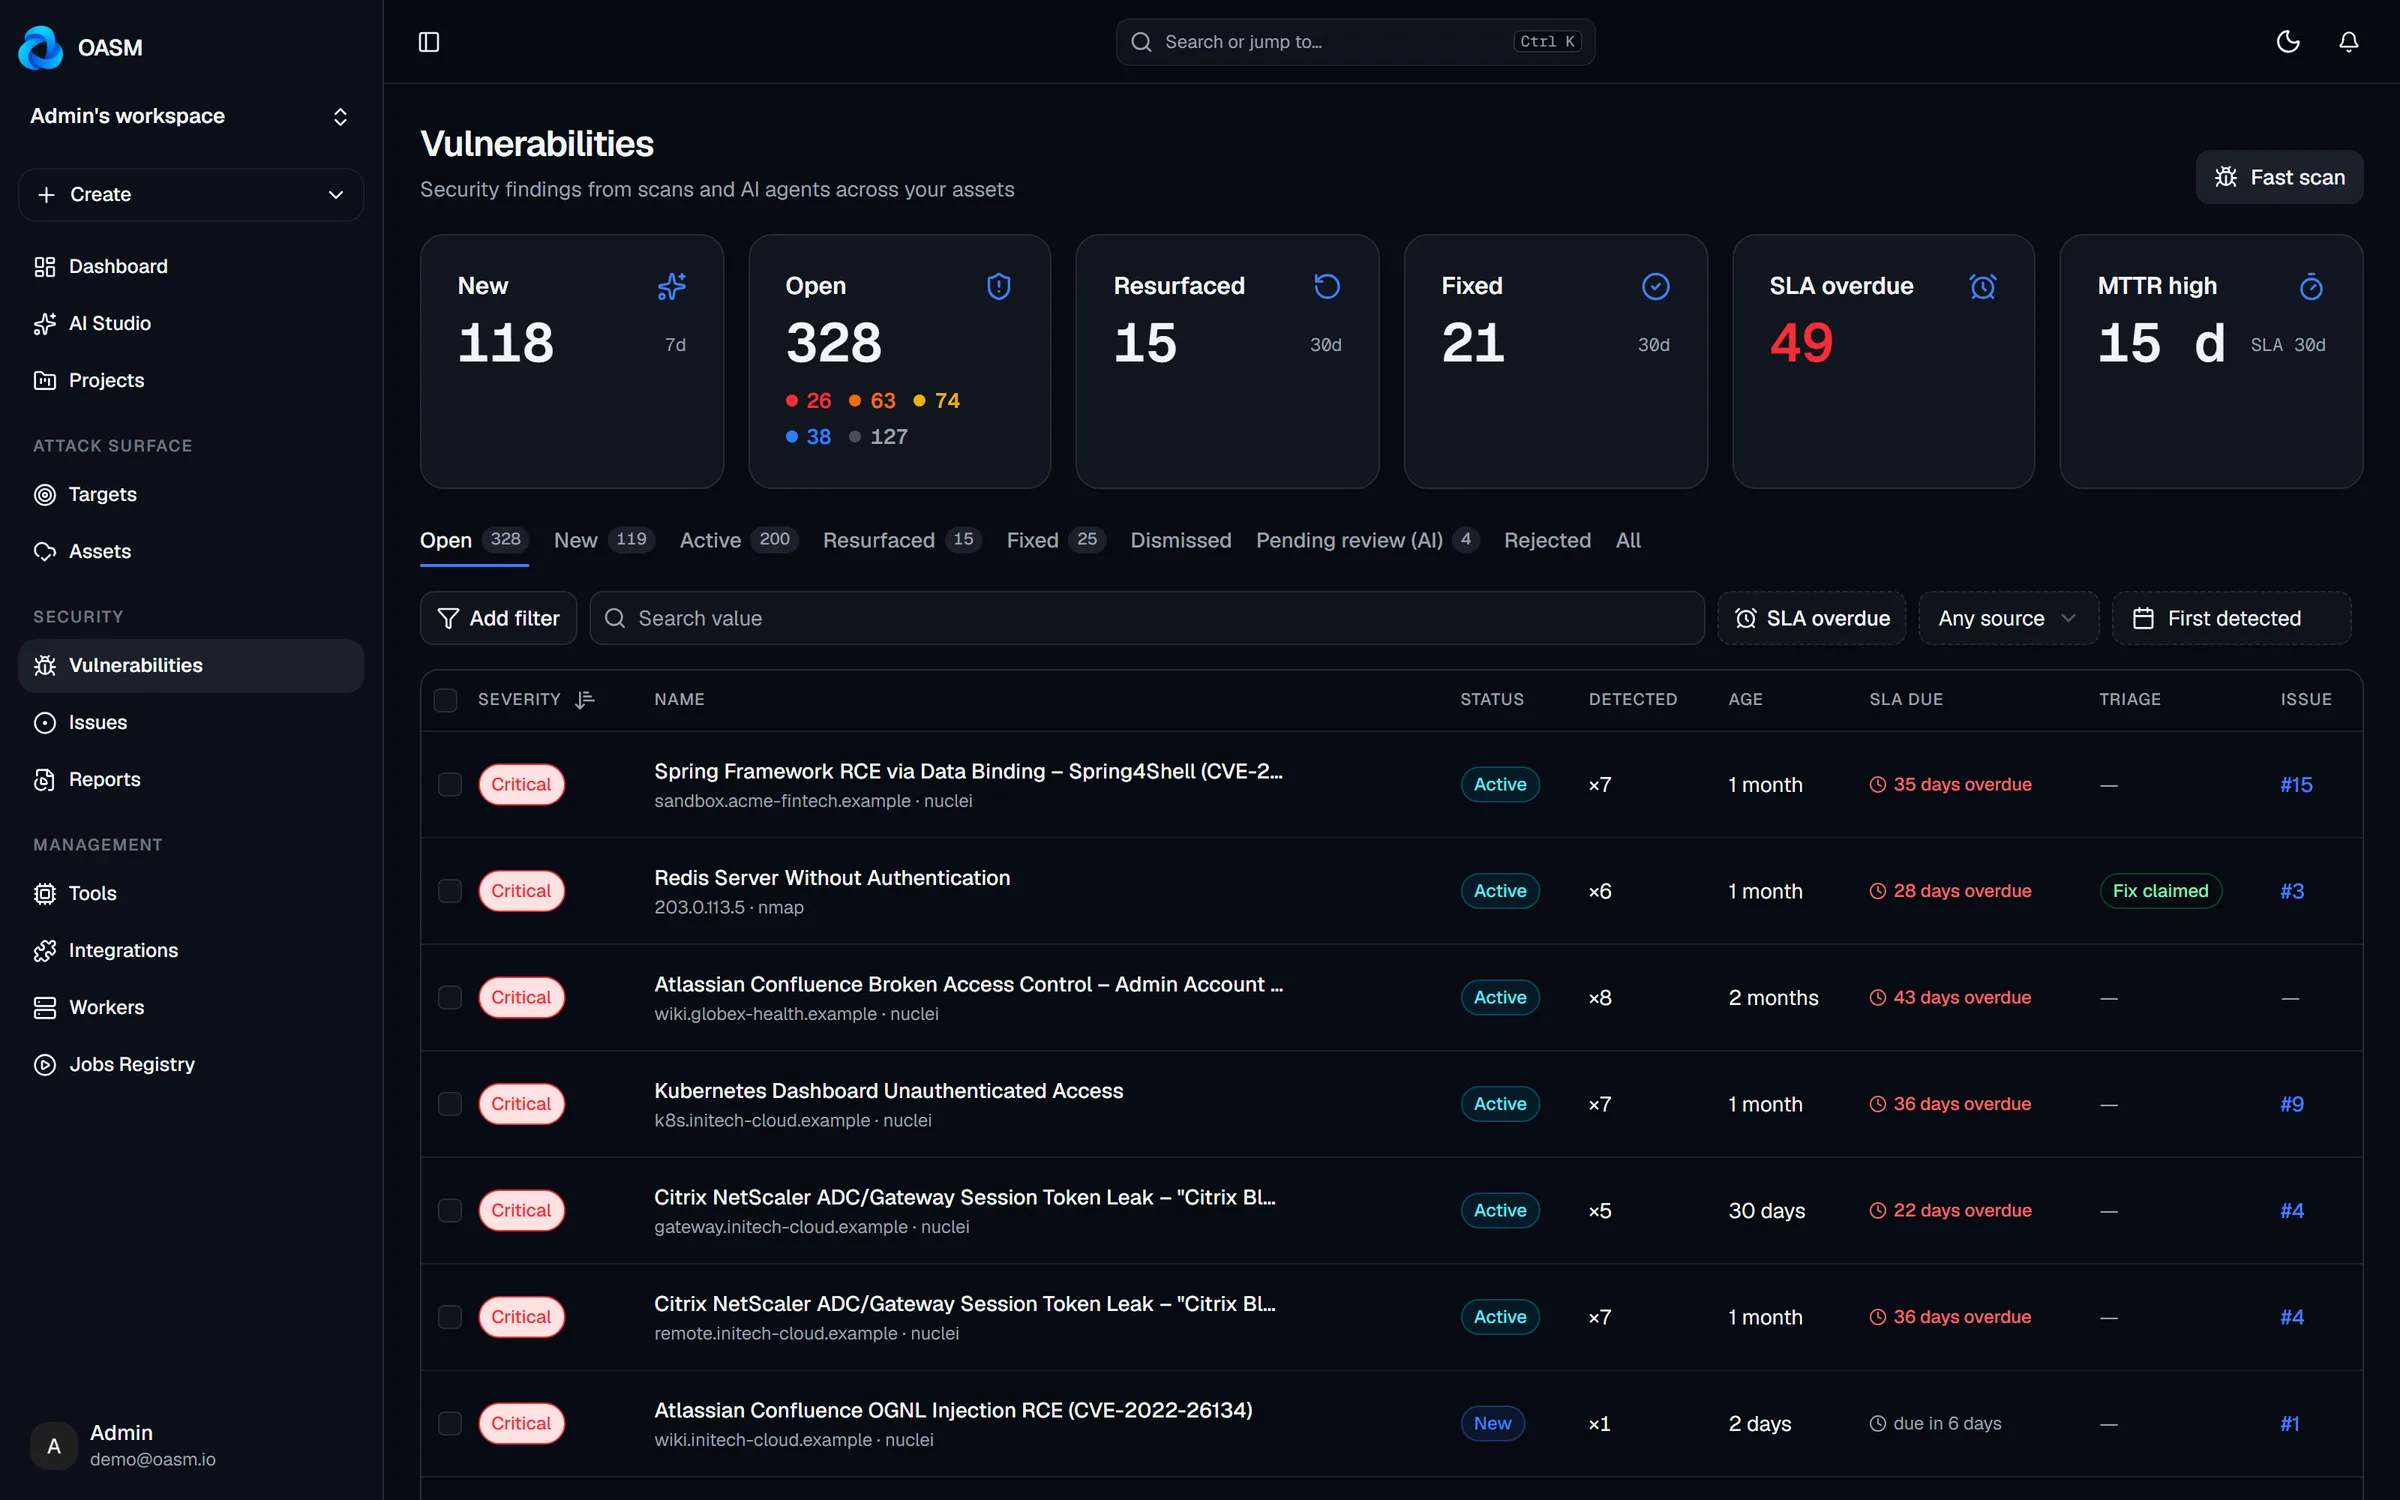
Open risk, at a glance
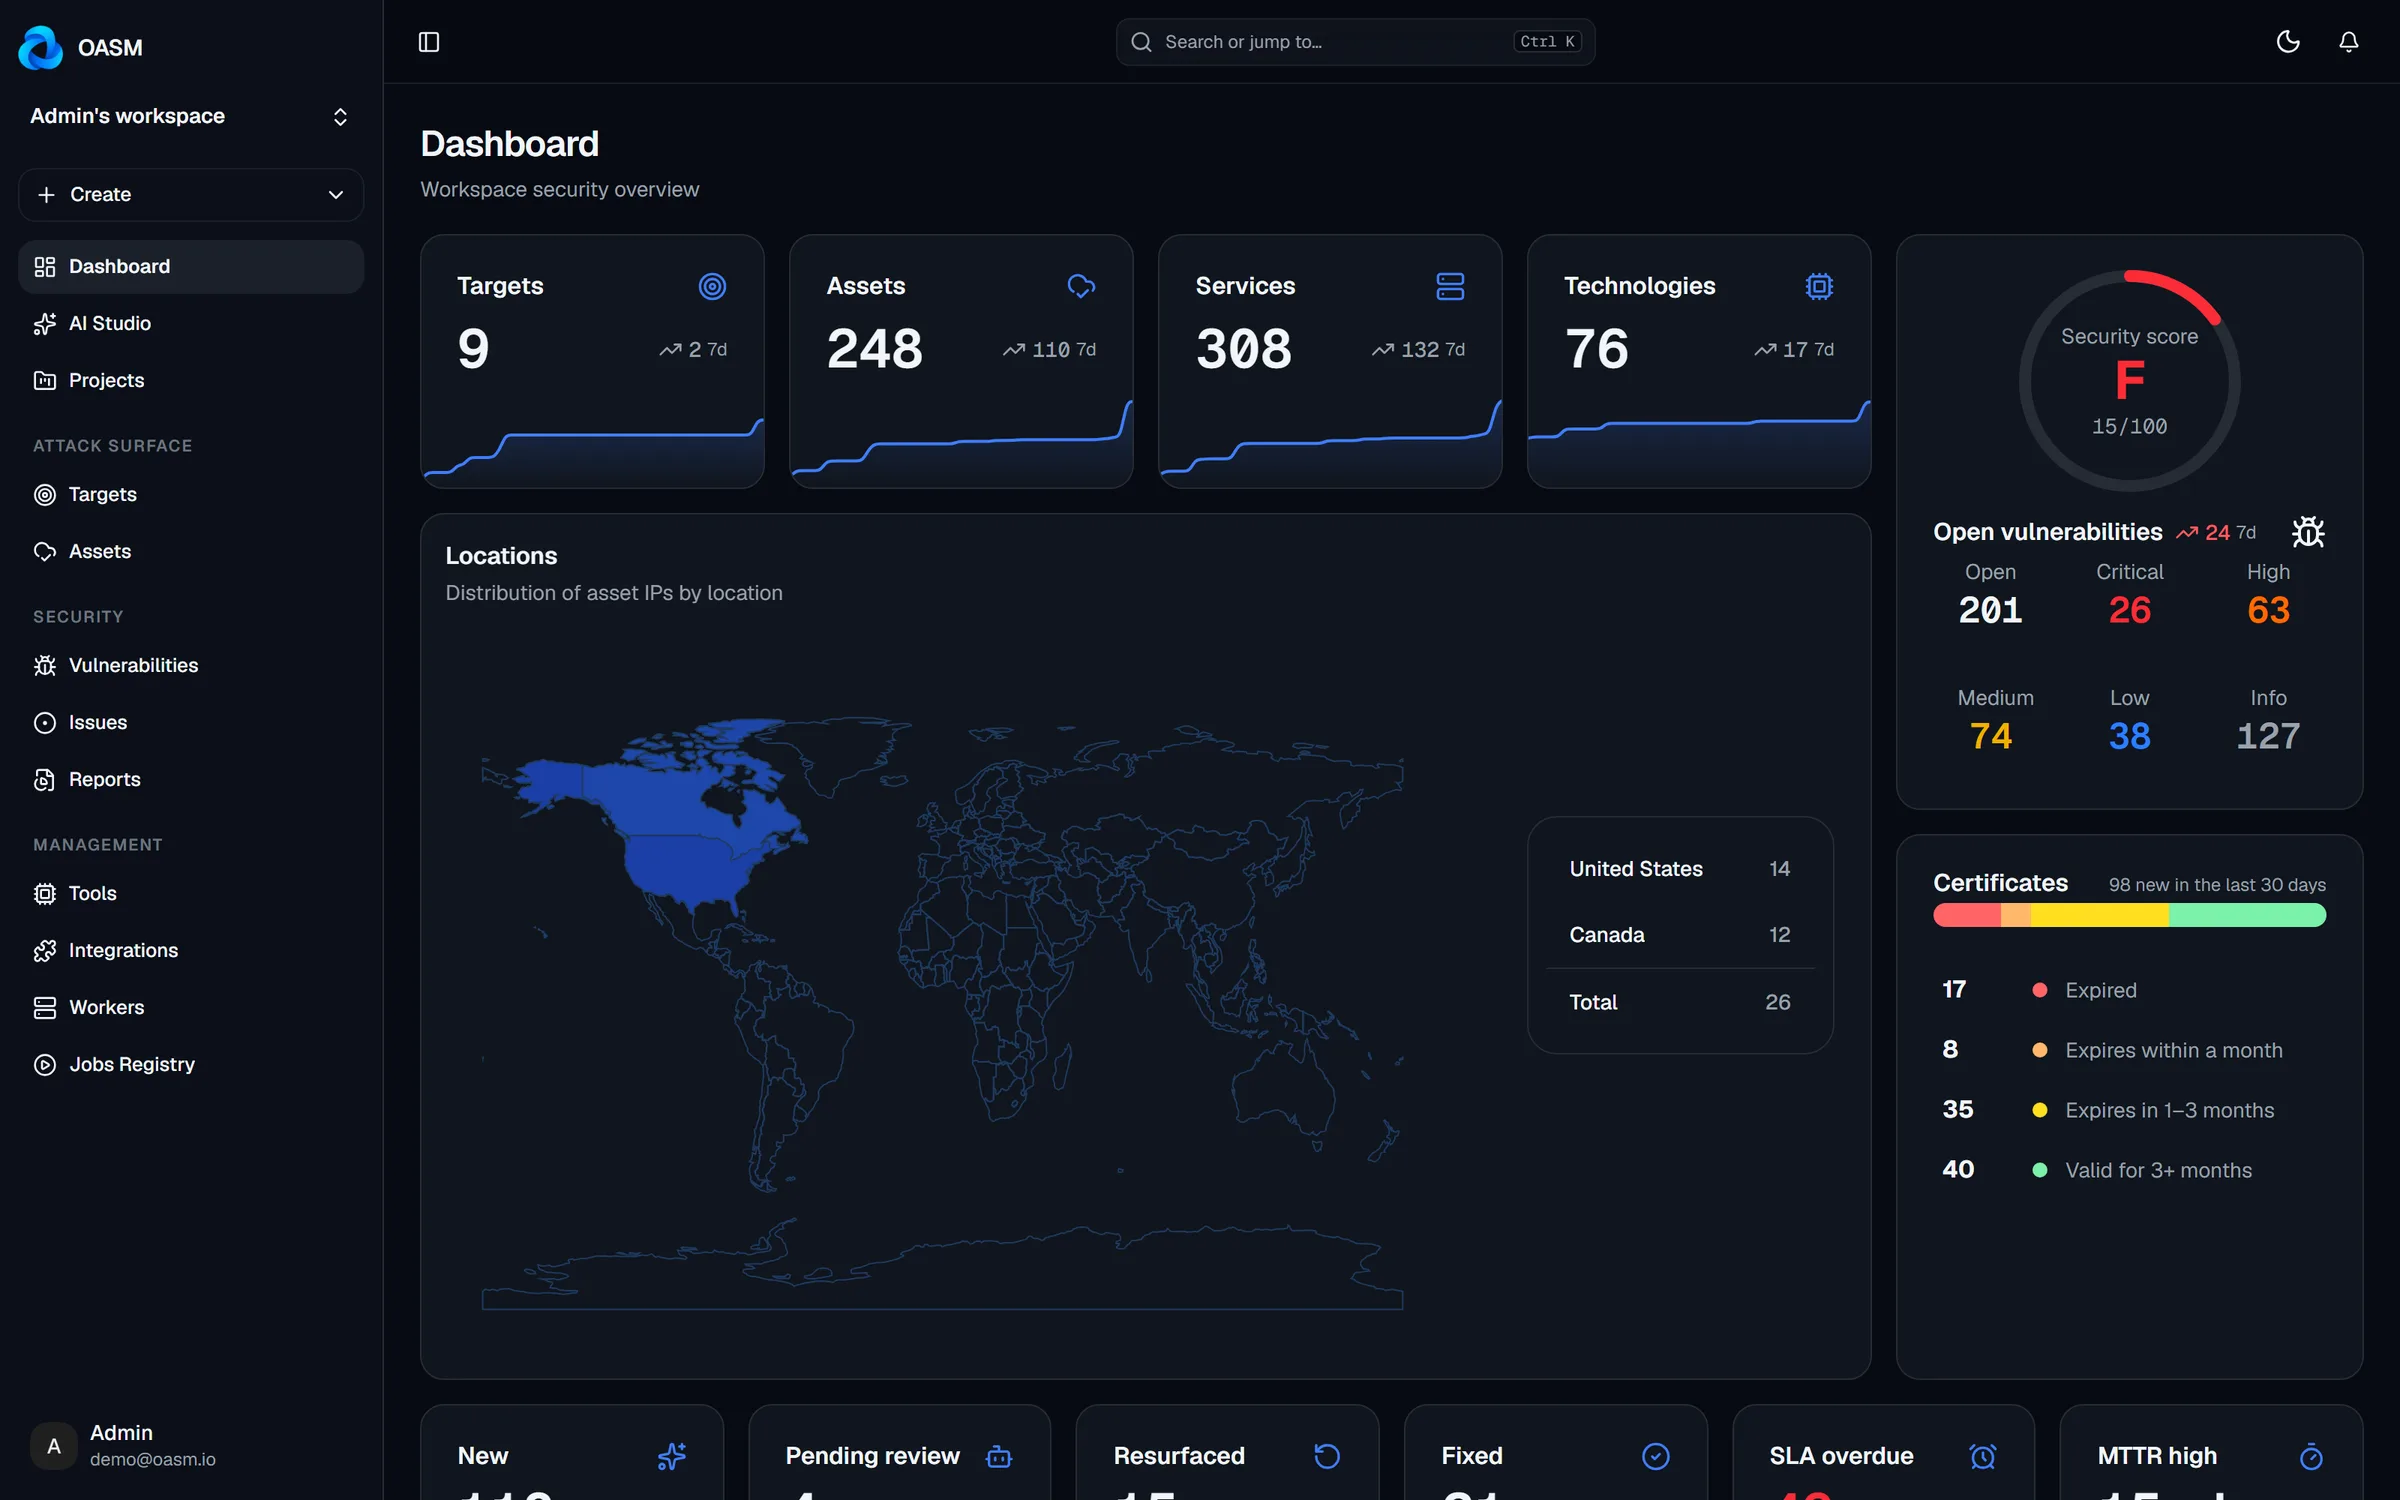
New, open, resurfaced, fixed, SLA overdue and MTTR in one strip.
Detect vulnerabilities and misconfigurations across every asset, rank them by real risk and let AI explain each one — with evidence checked against the raw scan output.
✓ Severity, CVSS and EPSS✓ SLA tracking and MTTR✓ AI analysis with evidence
THE PROBLEM
Hundreds of findings, five scanners, one week. Most teams fix what is loudest, not what is most dangerous. OASM ranks findings by real risk — and proves it.
Template, web-app and enterprise scanners write findings onto your real assets.
Duplicates merge, severity and SLA are set, and AI explains exploitability with evidence.
Assign, track, and watch resurfaced findings reopen on their own.
From a wall of raw findings to a short, defensible list of what to fix next.
New, open, resurfaced, fixed, SLA overdue and MTTR in one strip.
Scores, affected asset, proof and the fix — on one page.
AI claims are checked against the stored tool output.
Approve or reject AI-proposed findings in bulk.
Every severity has a deadline; overdue ones stand out.
Write Nuclei templates — or let AI Studio draft them.
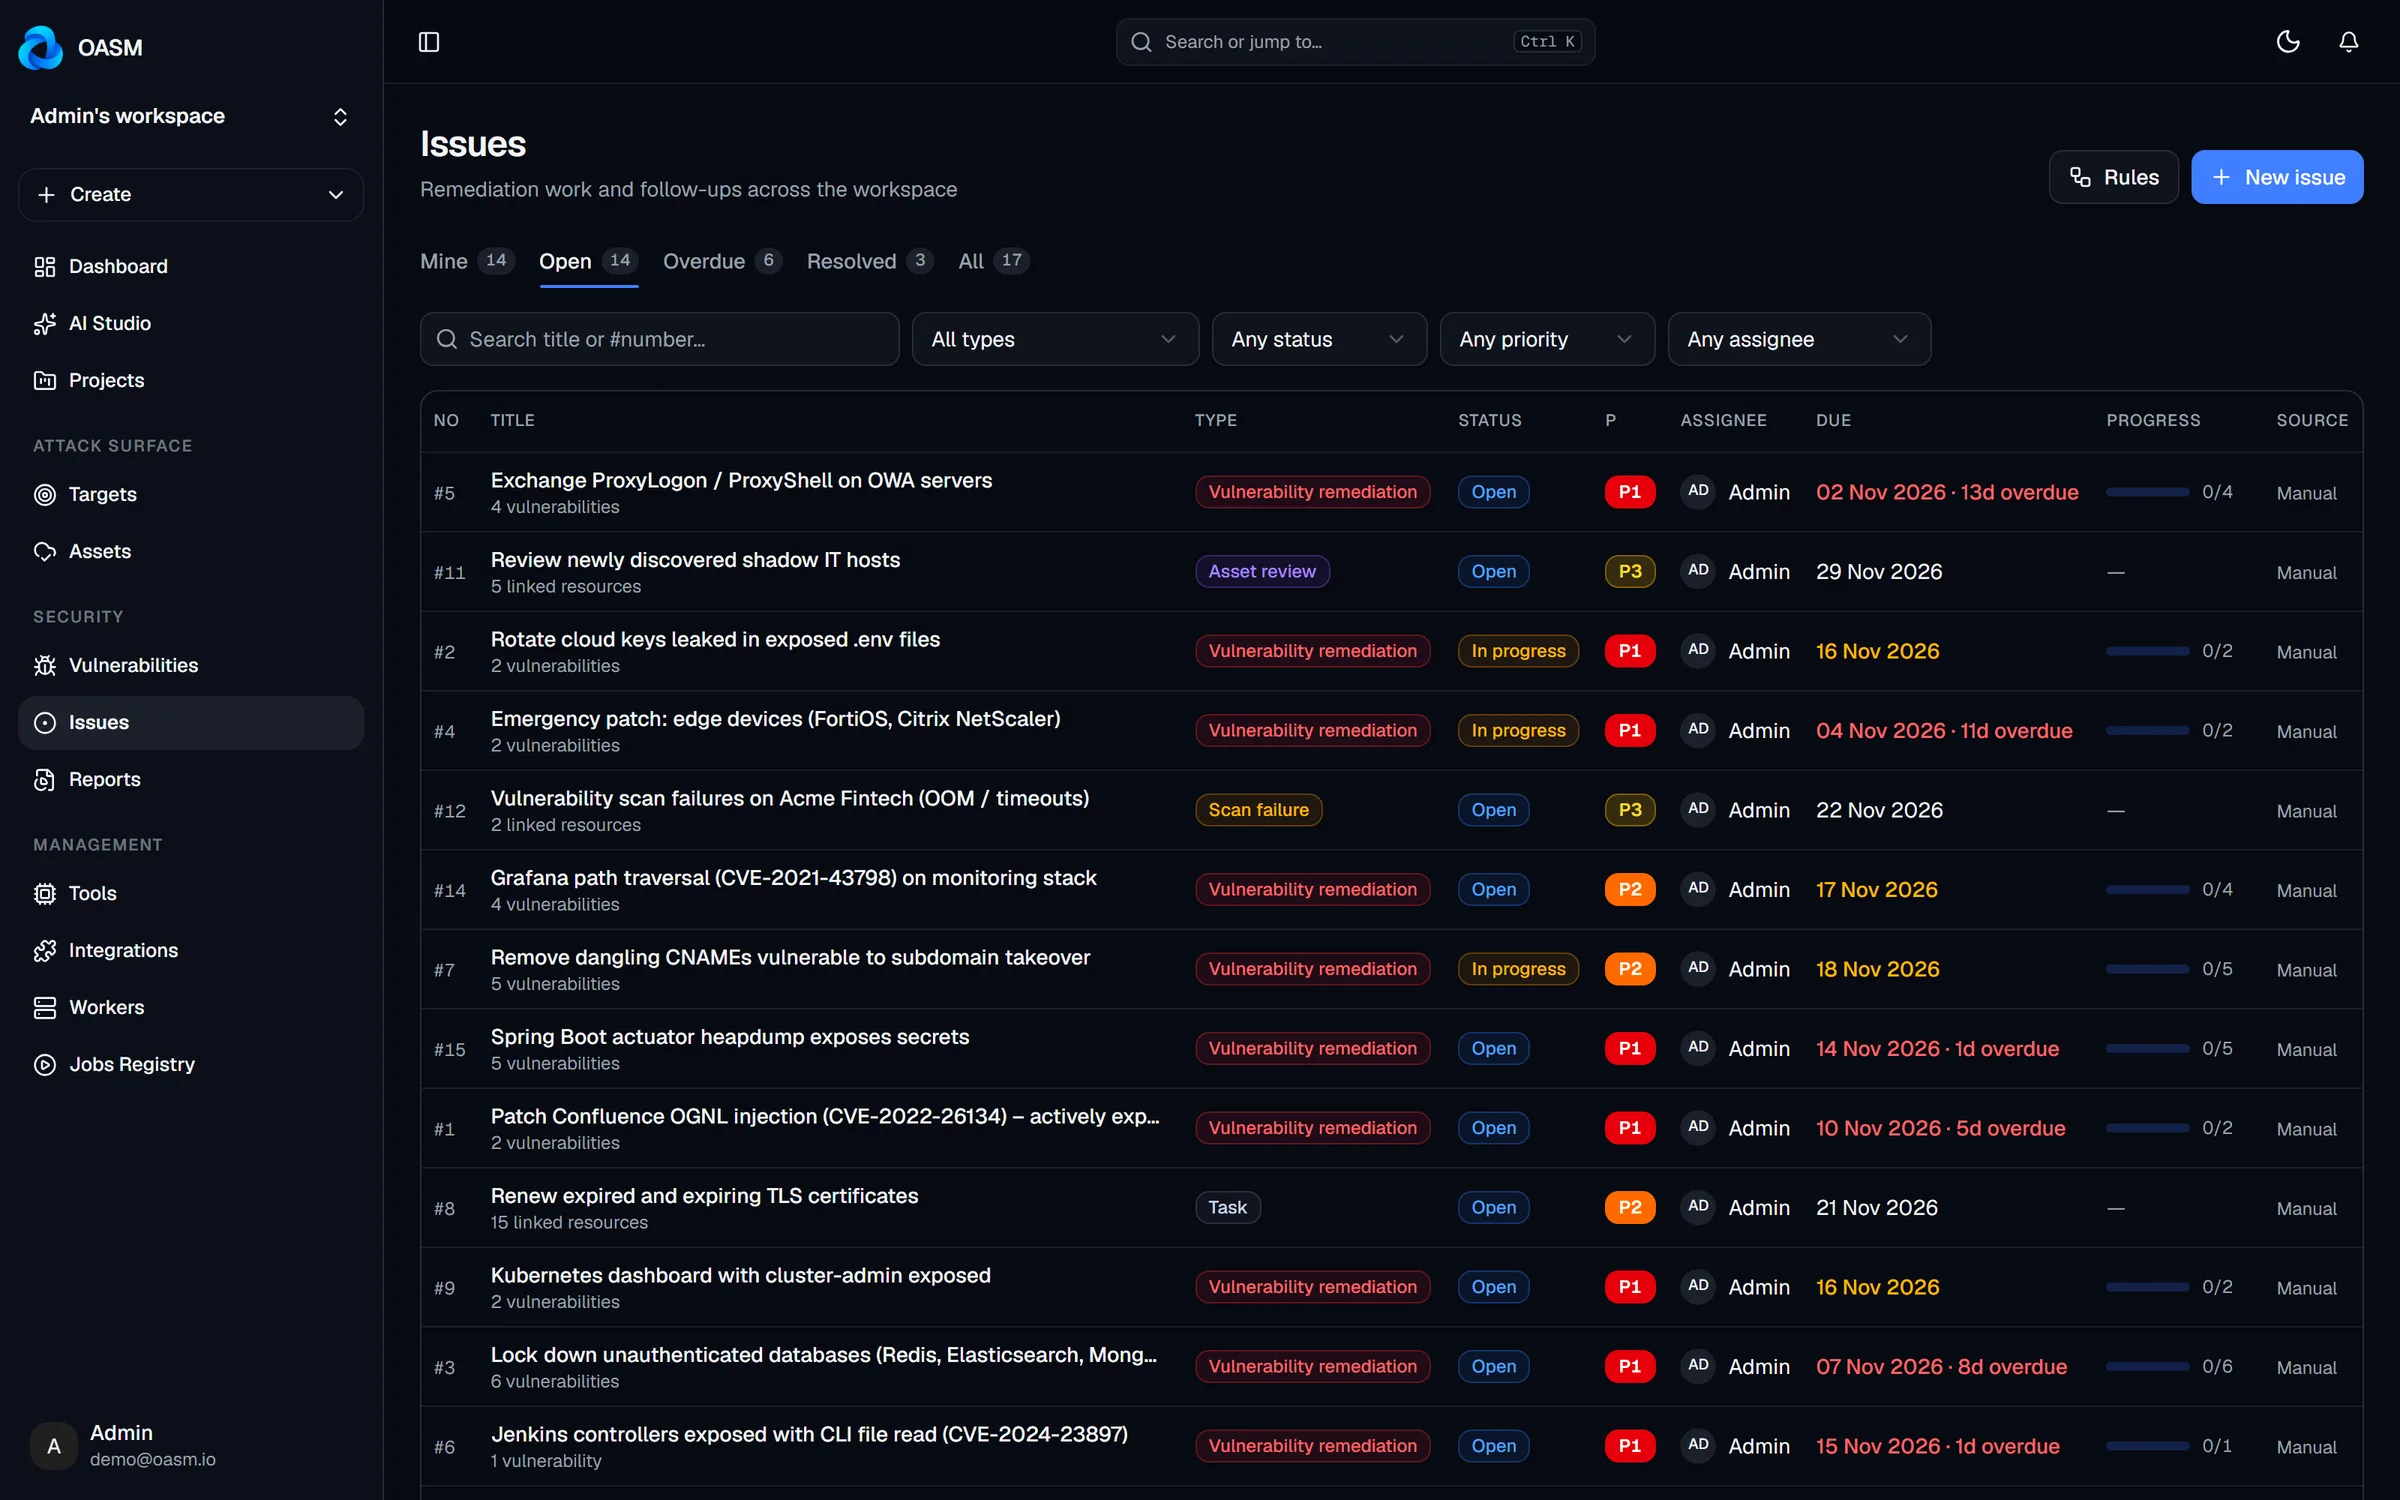
Each finding shows where it was found, what proves it and exactly how to remediate.
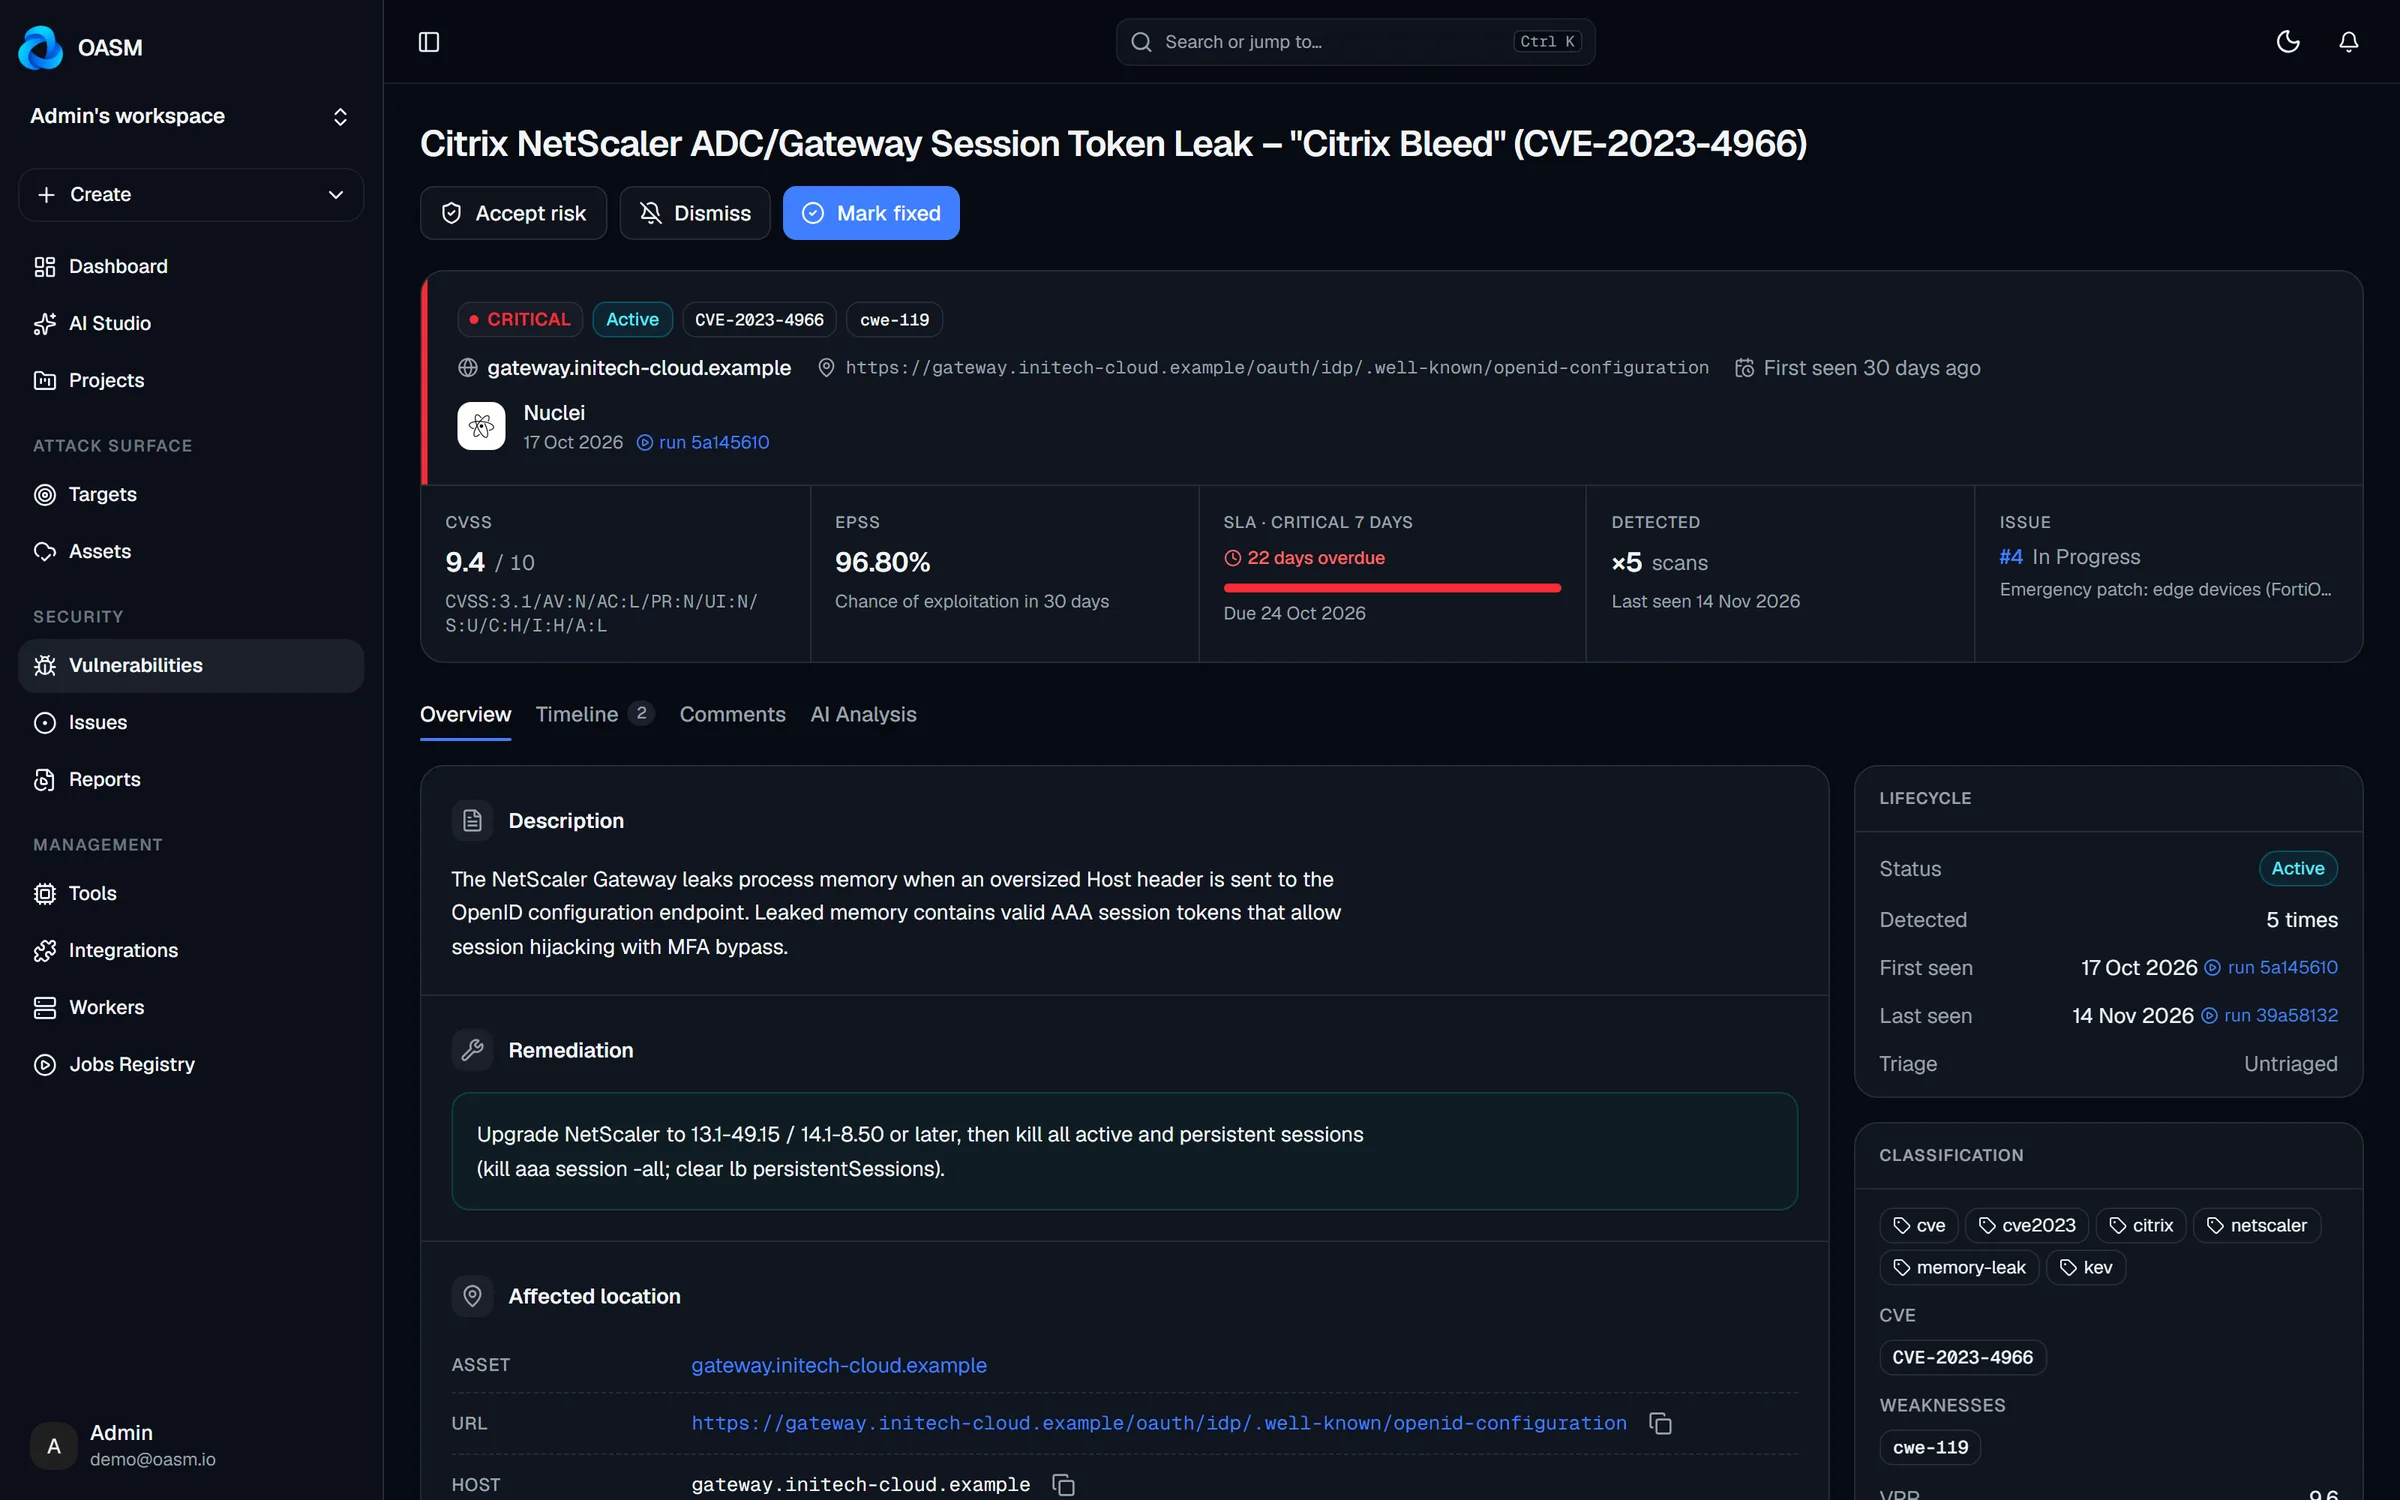
Projects get their own vulnerability view, SLA status and fix-first list.
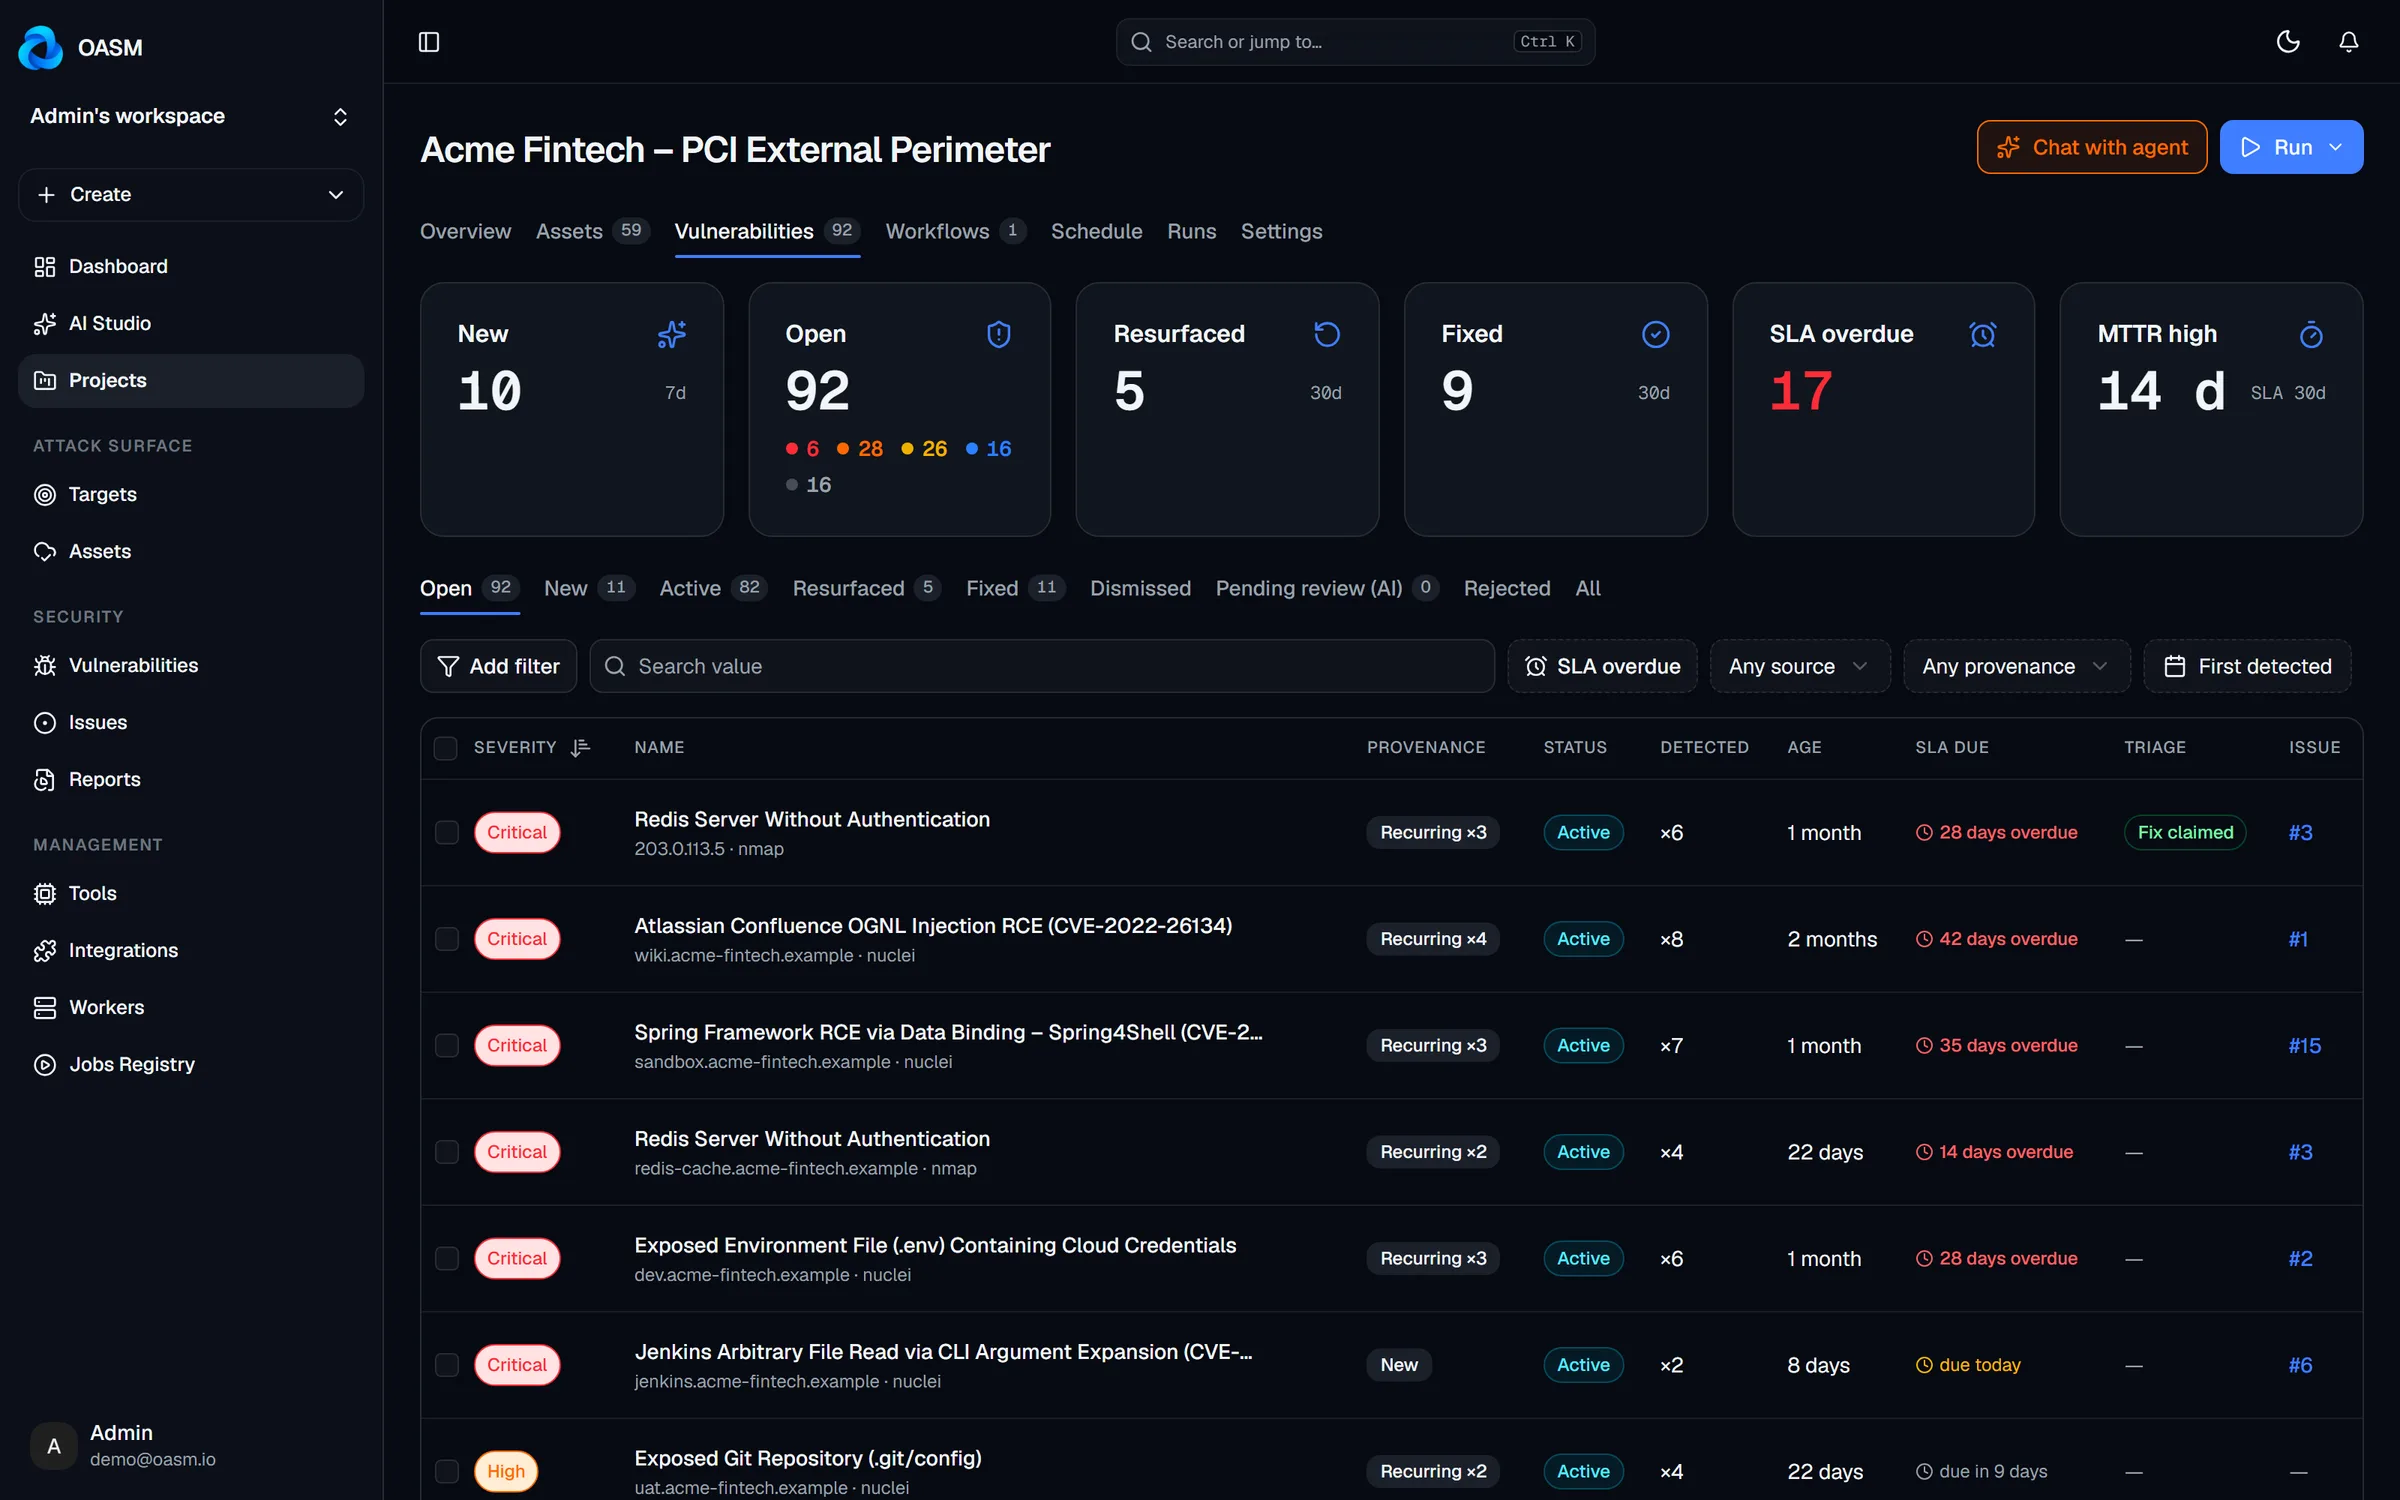
Deduplicated, risk-ranked findings with clear owners and deadlines.
Evidence and AI analysis make every ticket easy to act on.
SLA compliance and MTTR show whether risk is really going down.
Any installed scanner connector — template-based, web-app and enterprise scanners. See the Marketplace.
Free, open source and self-hosted. Your data never leaves your infrastructure.