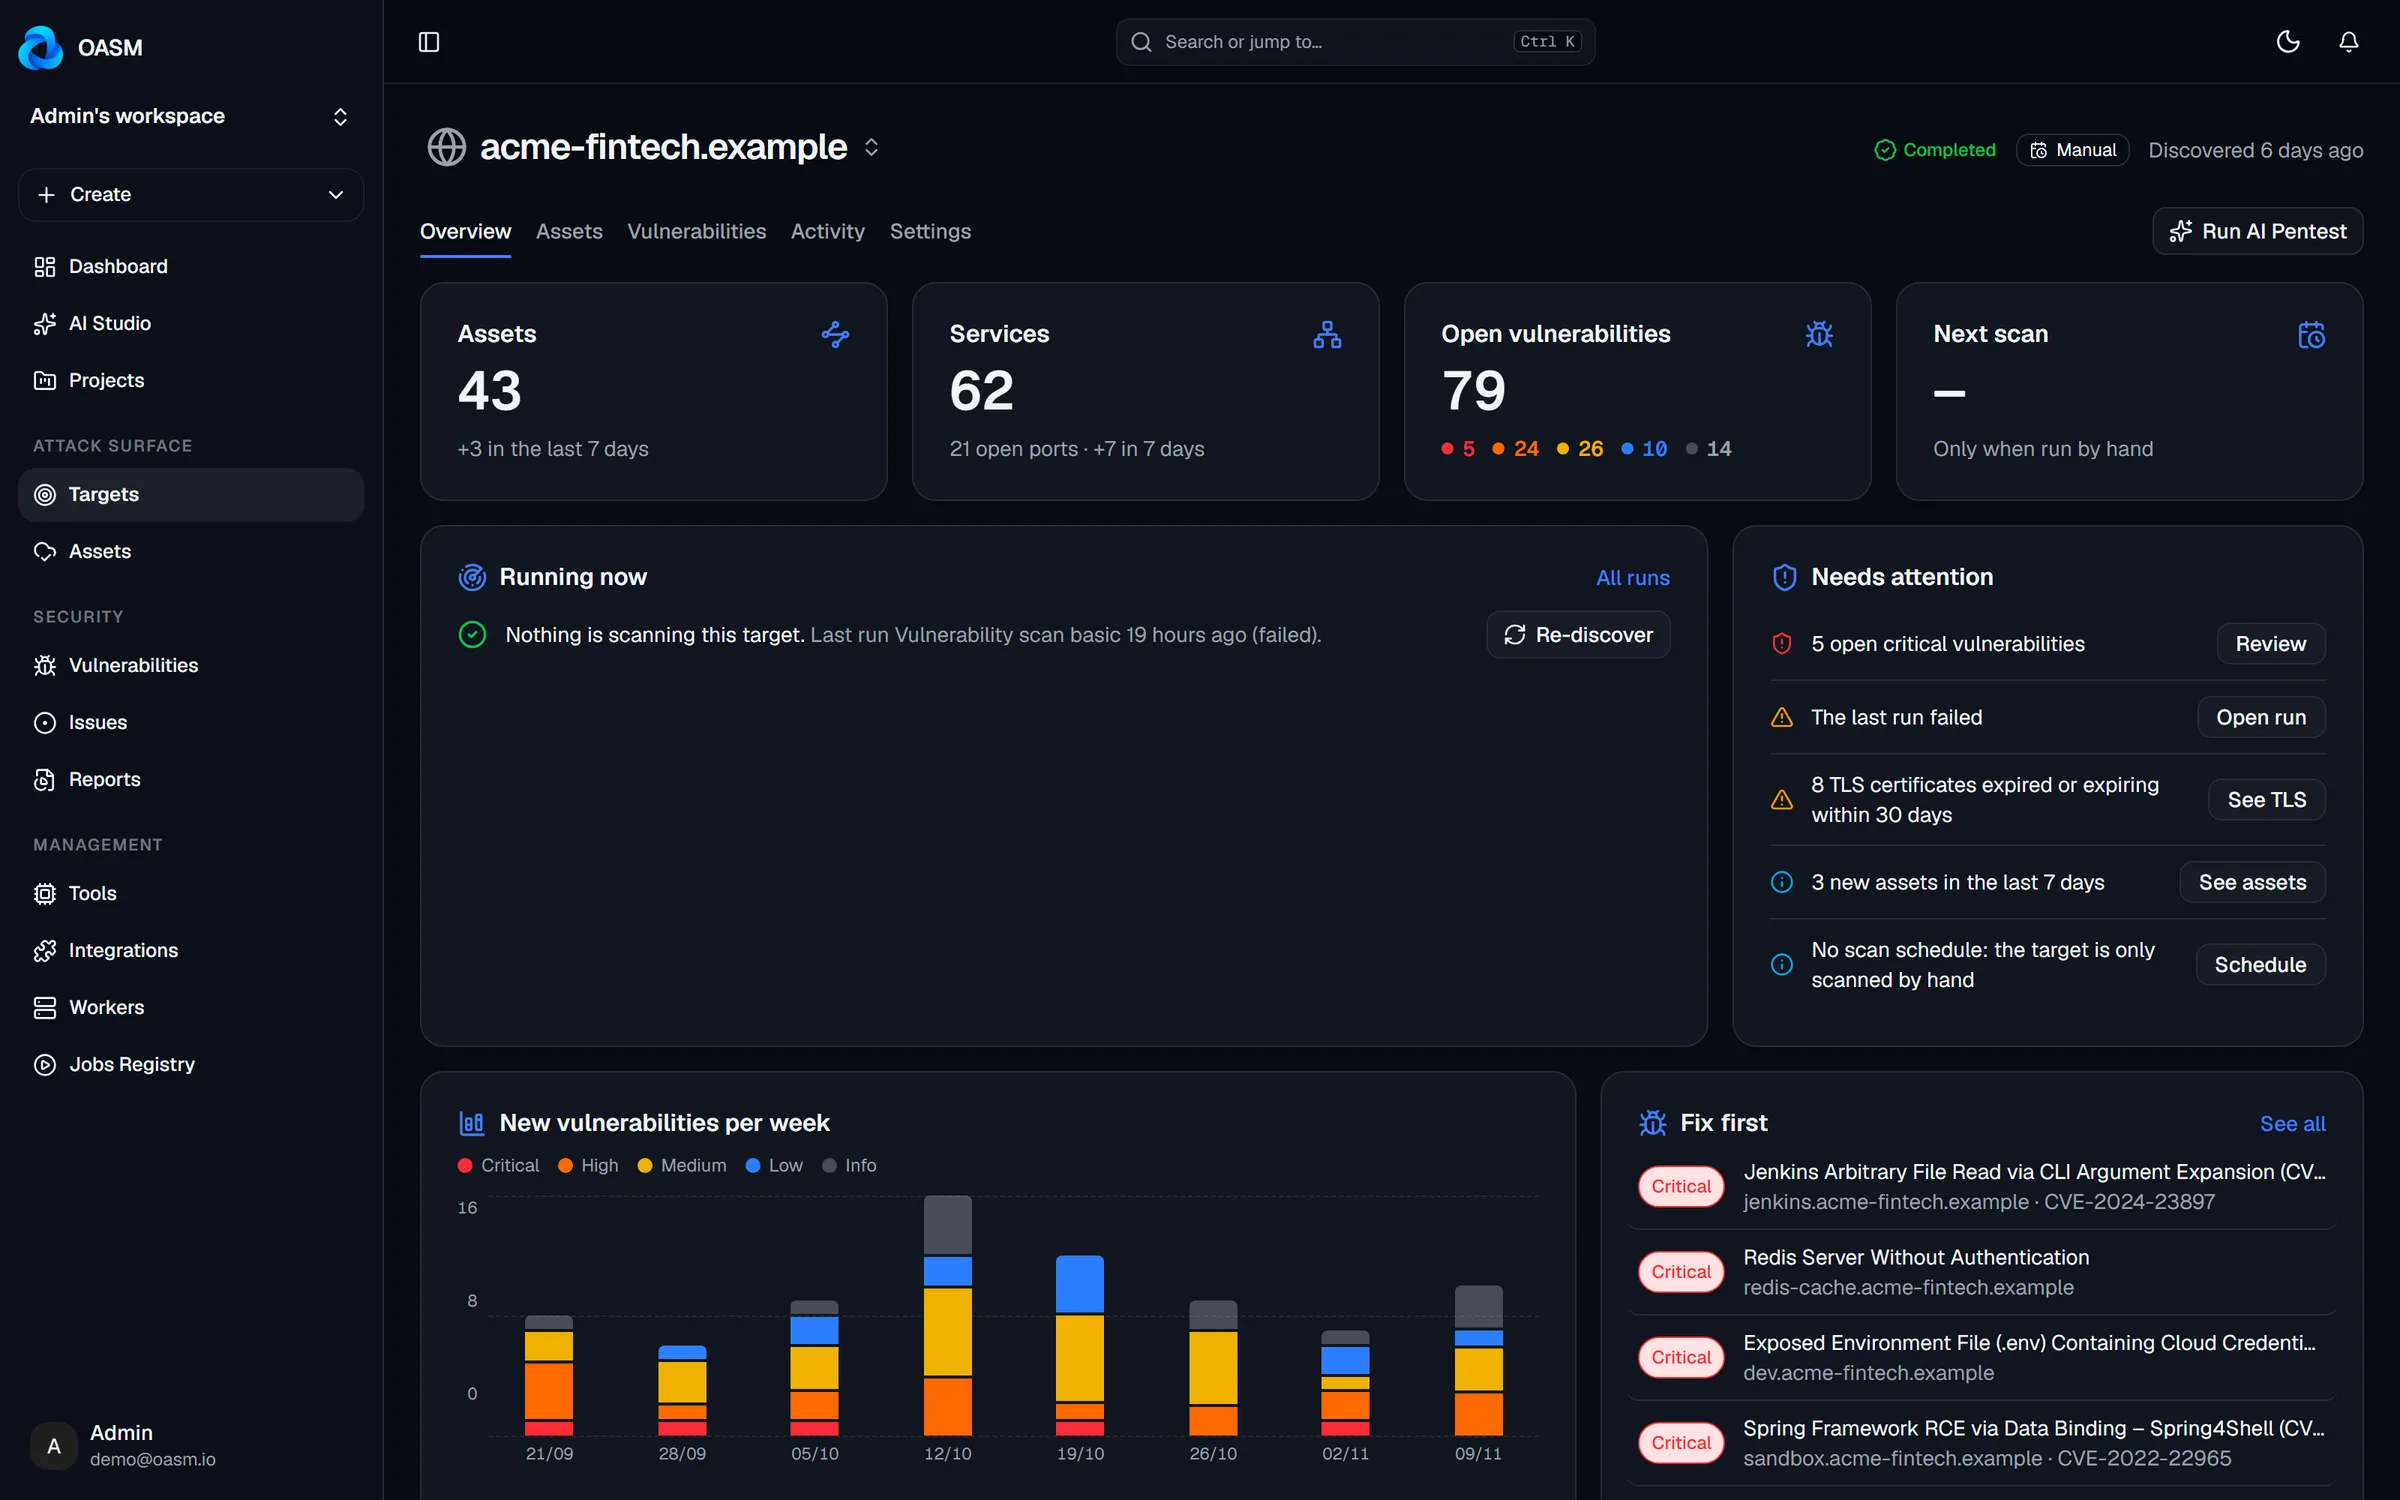
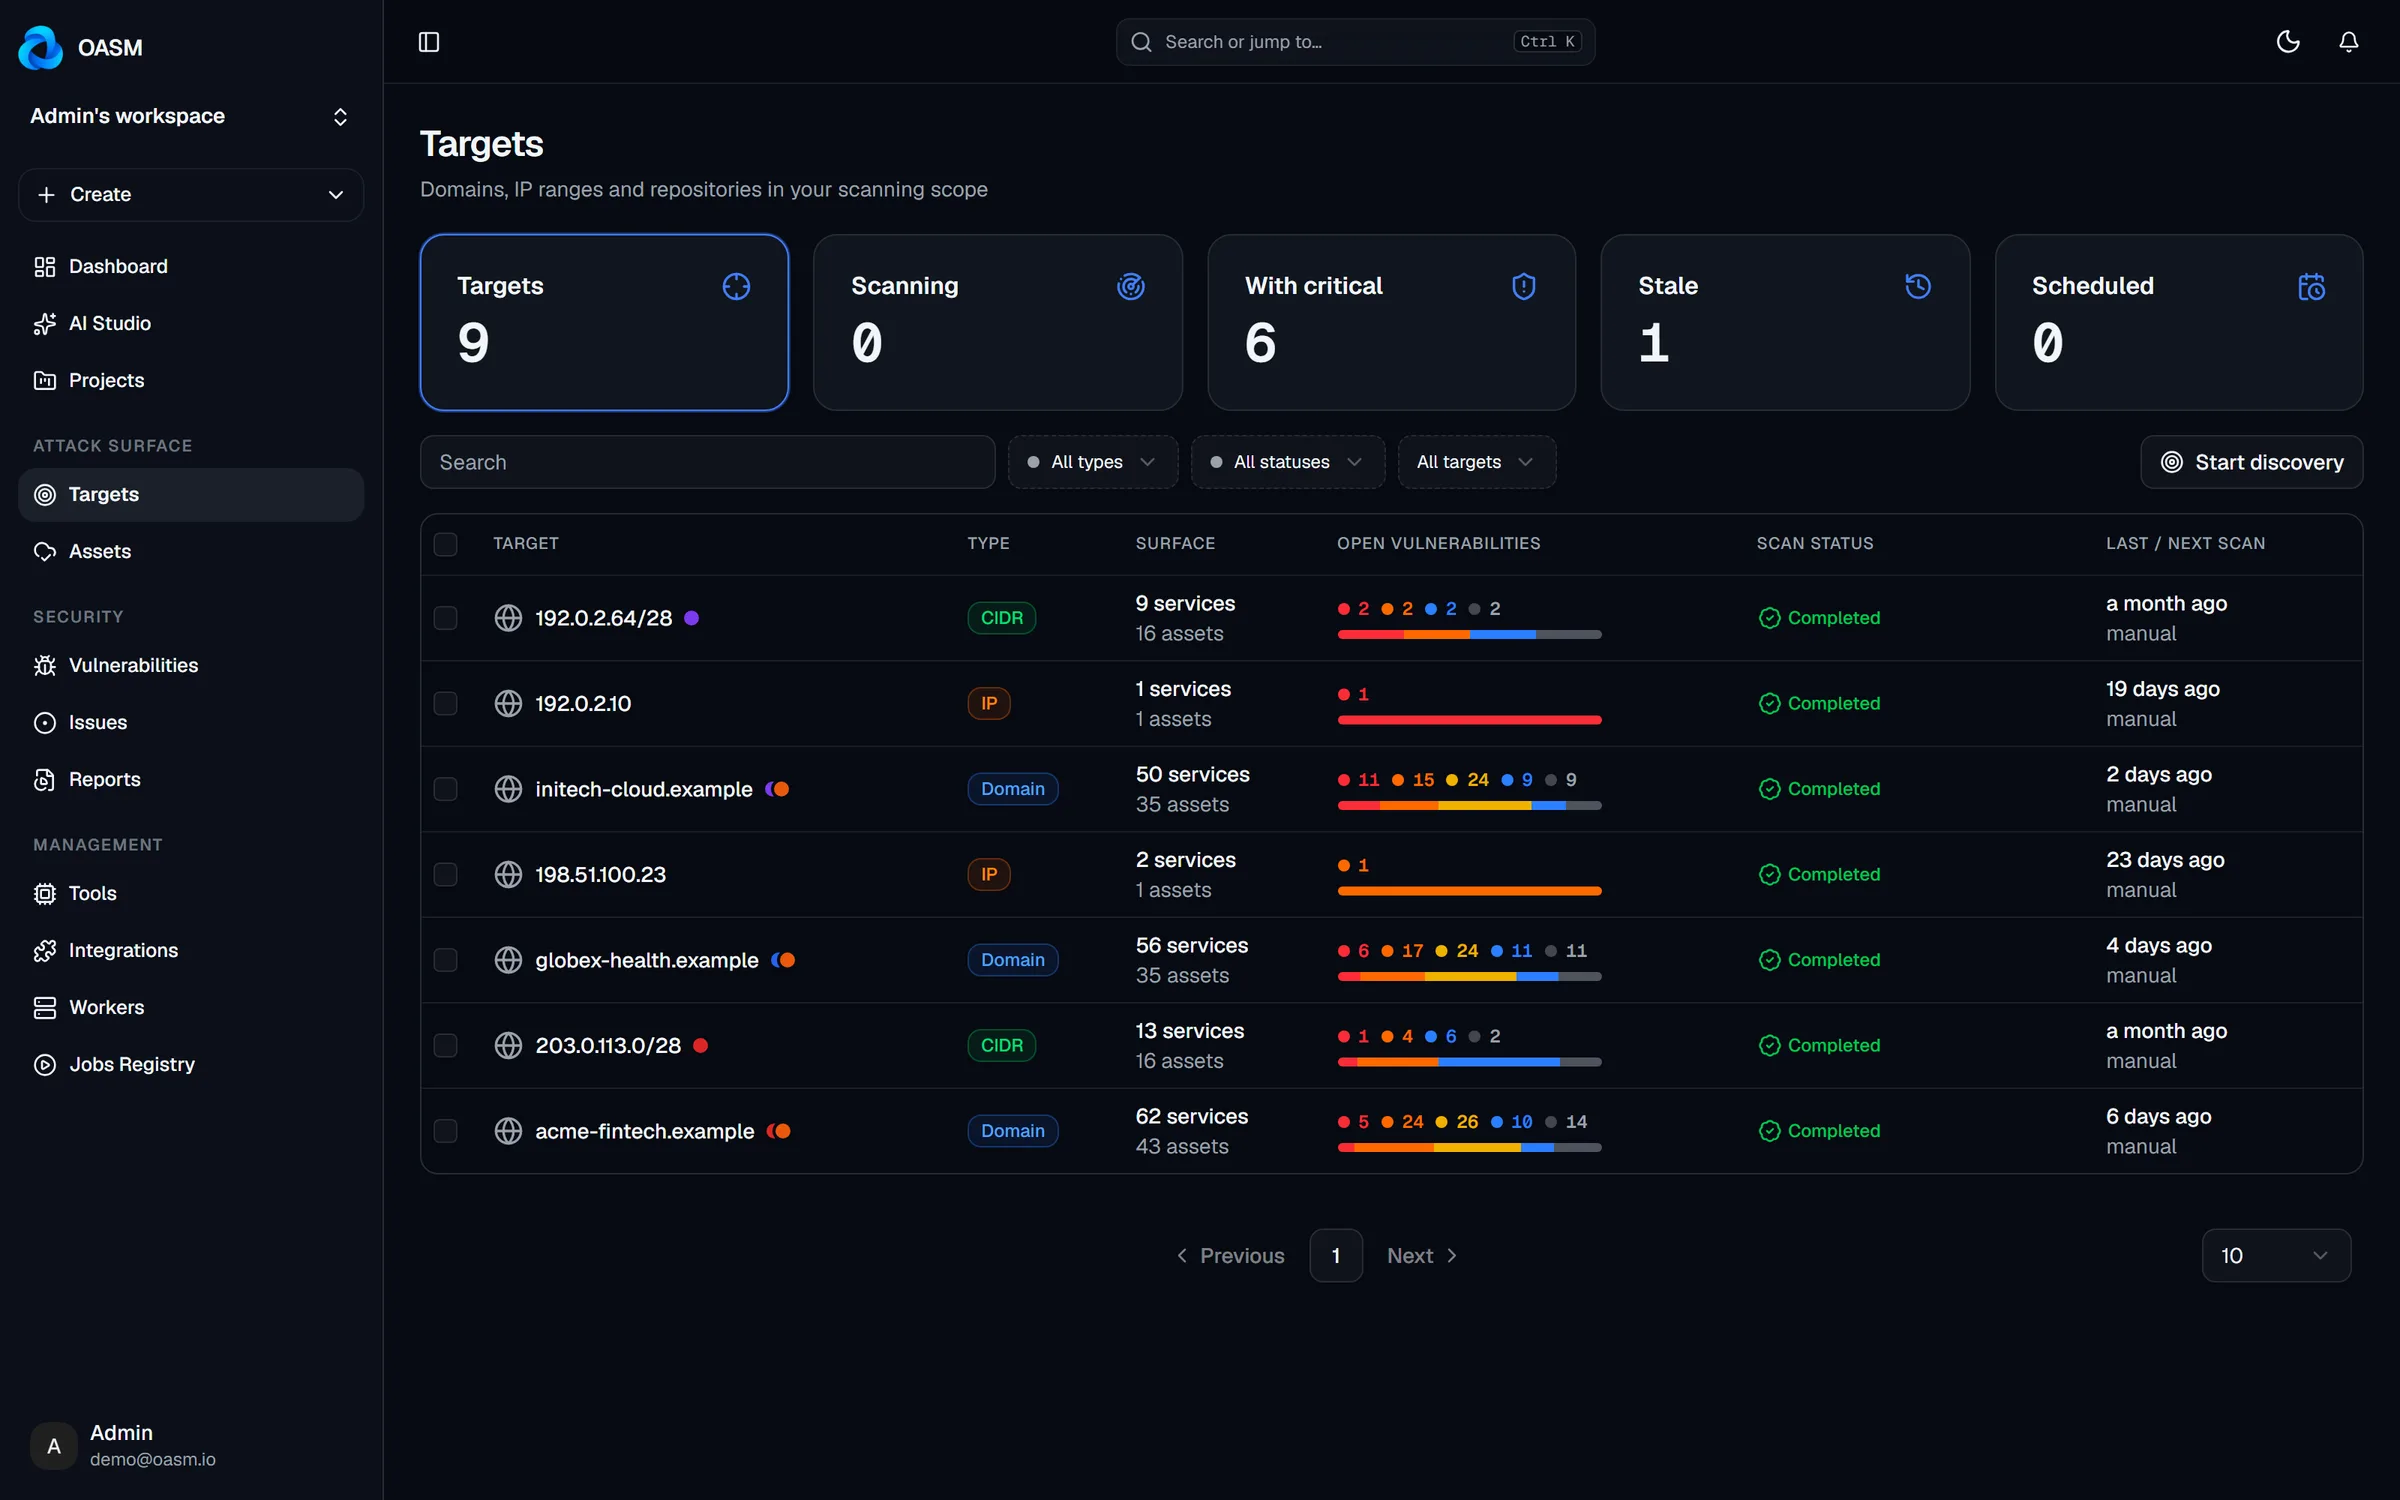
A scorecard per target
Assets, services, open vulnerabilities and what needs attention — on one screen.
Start from a domain, an IP or a CIDR. OASM expands it into subdomains, open ports, live services and screenshots — and keeps re-checking on your schedule.
✓ Domains, IPs, CIDRs and repositories✓ Cloud accounts feed assets in✓ Free and self-hosted
THE PROBLEM
A developer spins up a test box on Friday. Marketing launches a campaign domain on Monday. Your real attack surface is always bigger than the spreadsheet. OASM finds it for you — automatically.
A root domain, a single IP, a CIDR range or a repository — or connect a cloud account.
Subdomains are enumerated, ports scanned, HTTP probed and every page screenshotted.
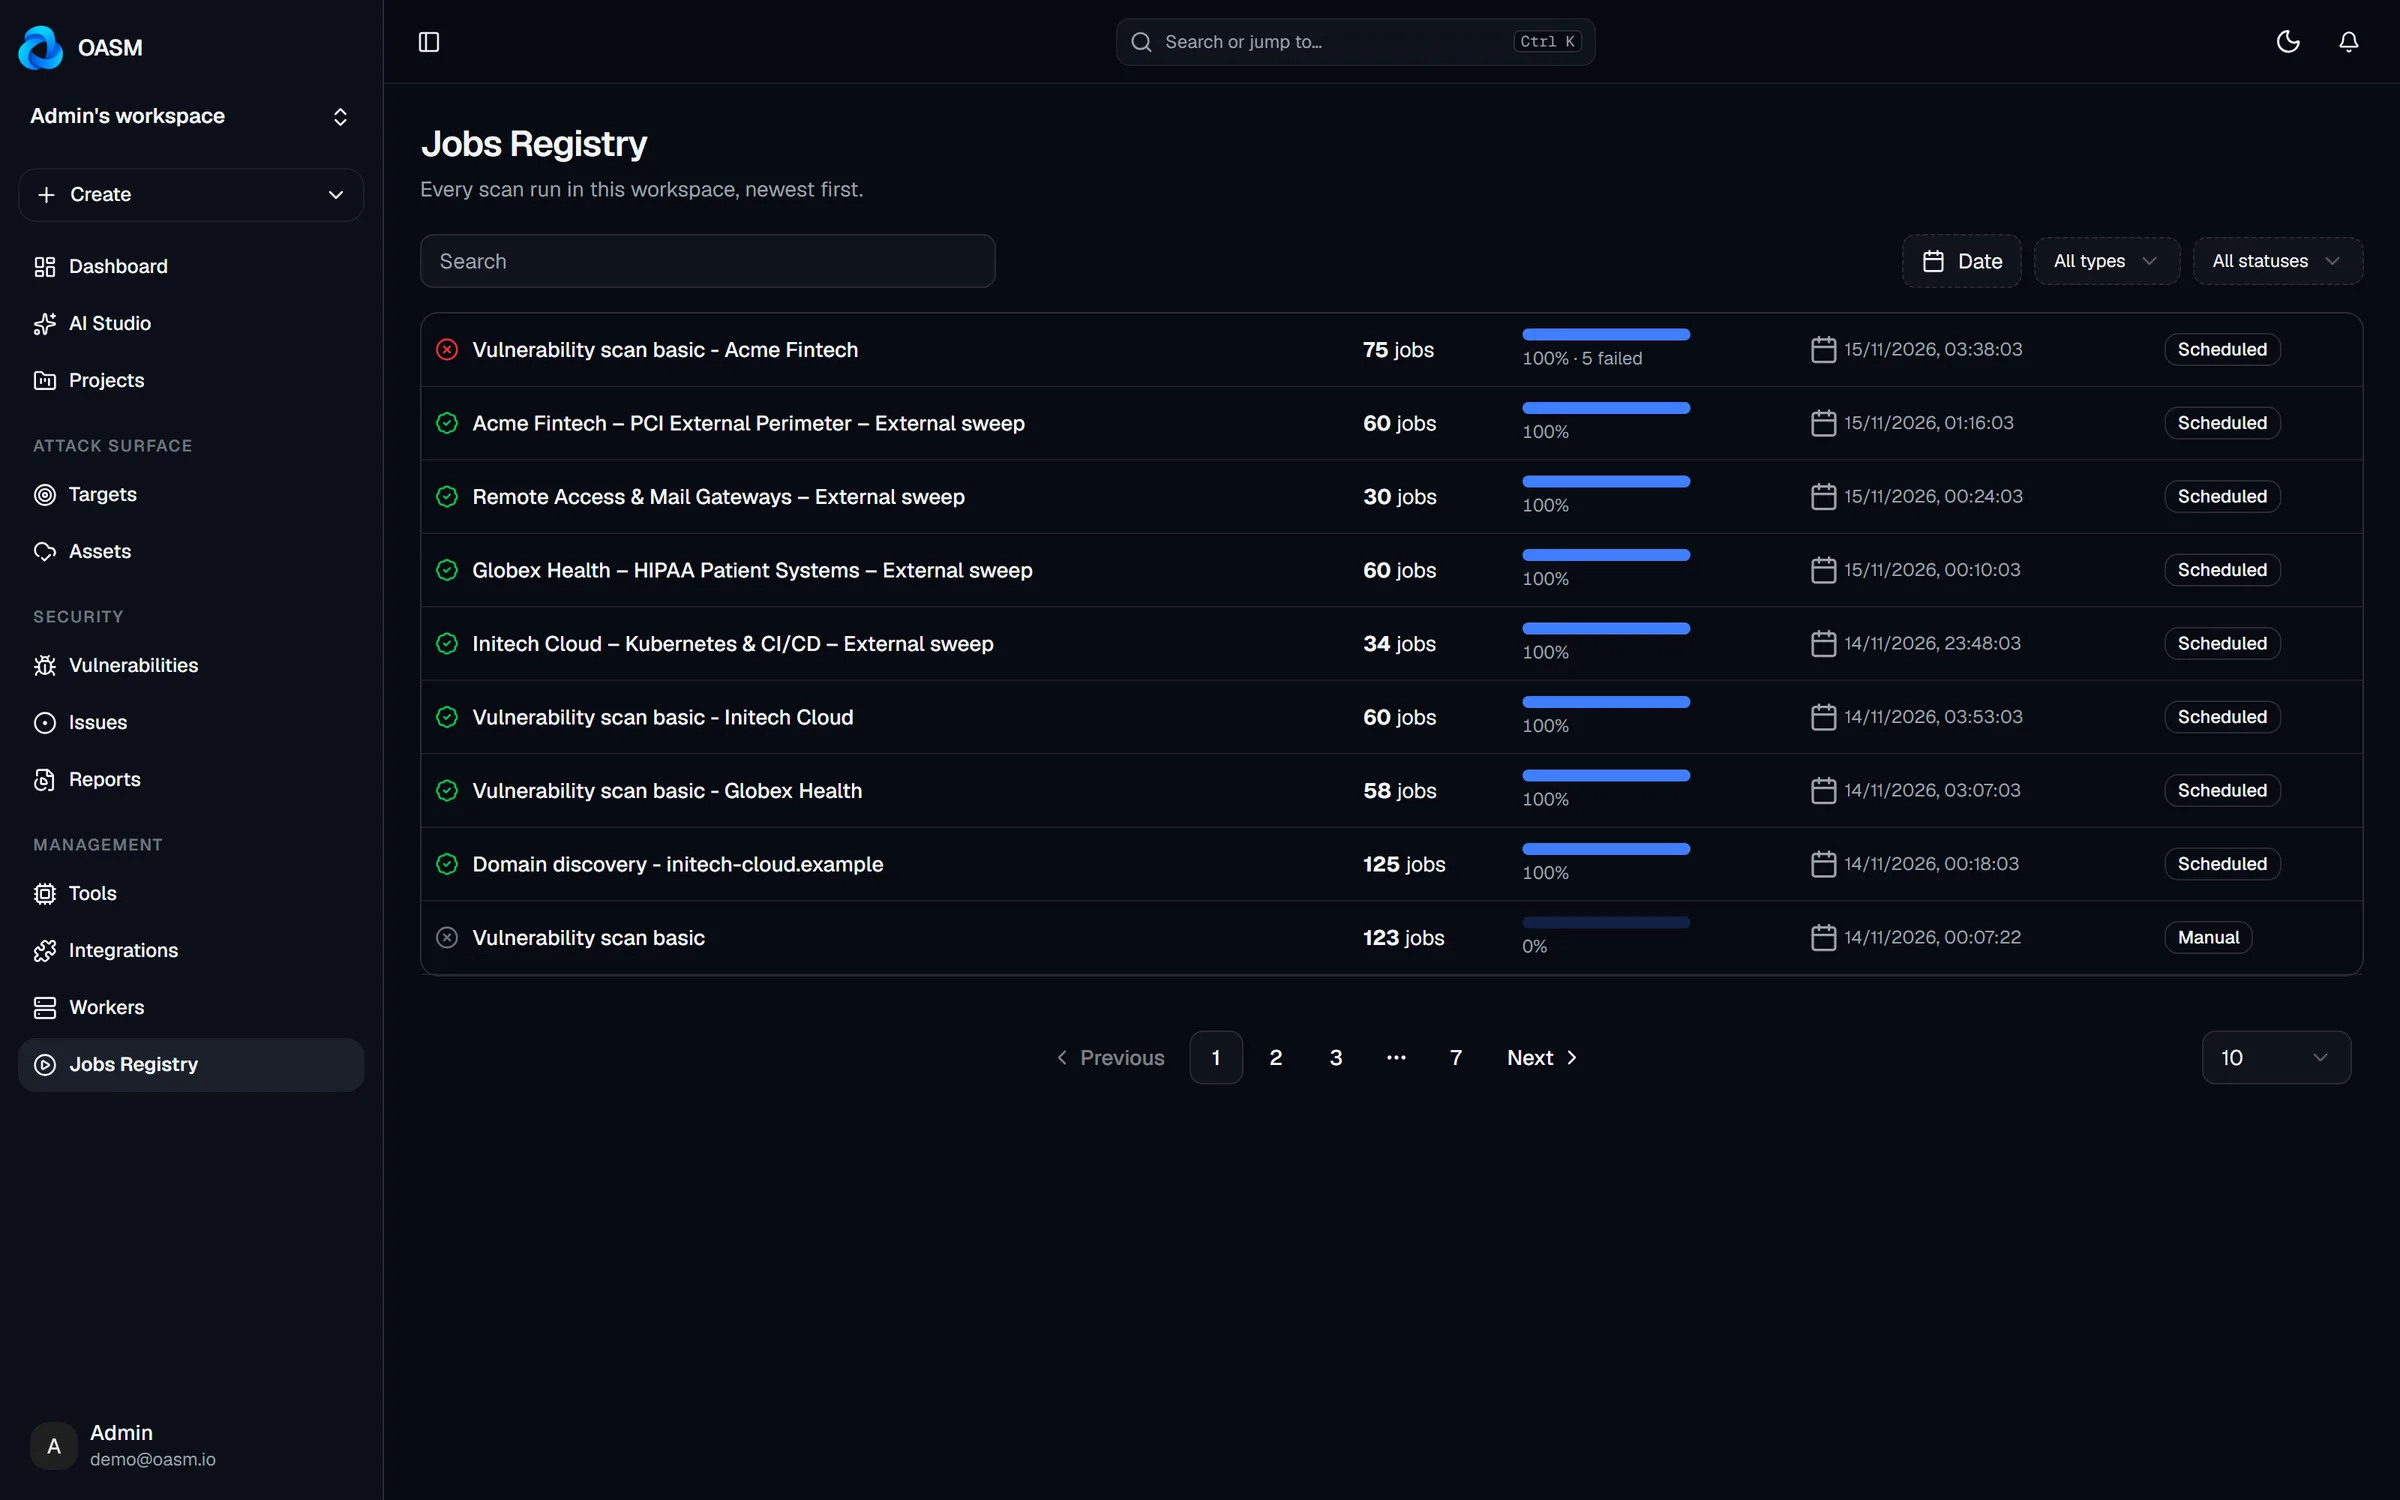
Schedules re-run discovery and flag new hosts, new ports and stale targets.
Each target becomes a living picture of what it exposes, refreshed on every run.
Assets, services, open vulnerabilities and what needs attention — on one screen.
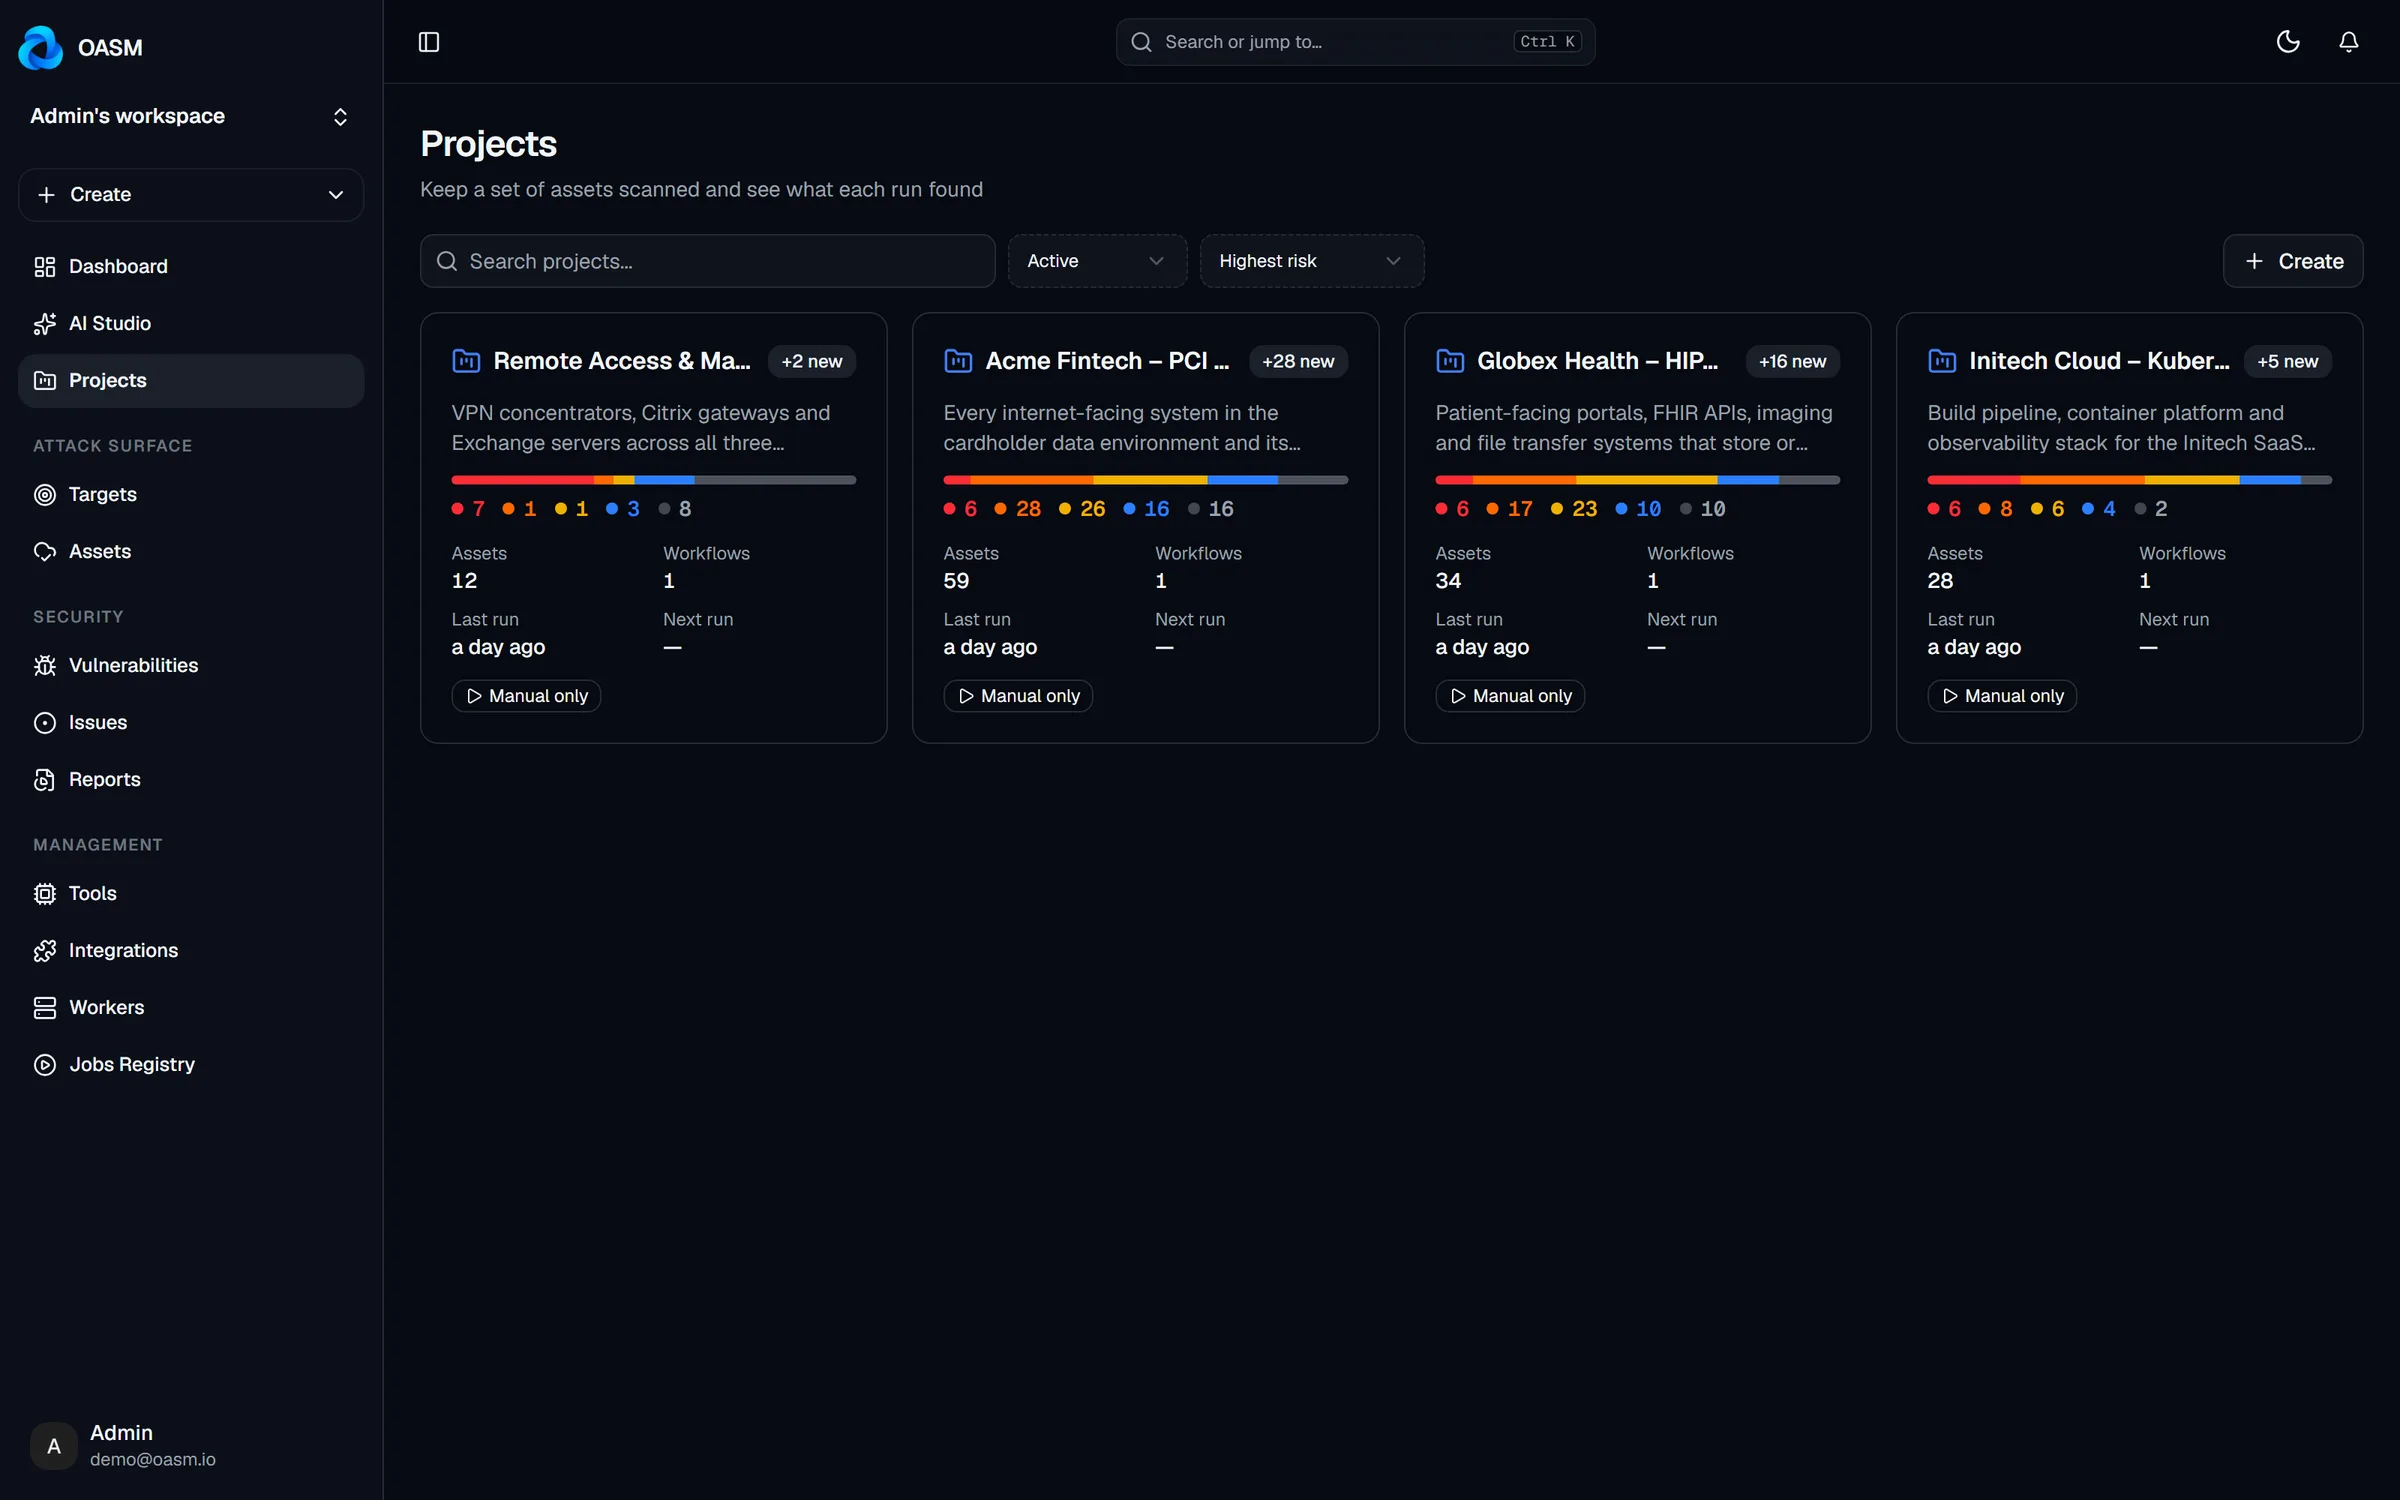
Compare targets by surface size, open findings and scan status.
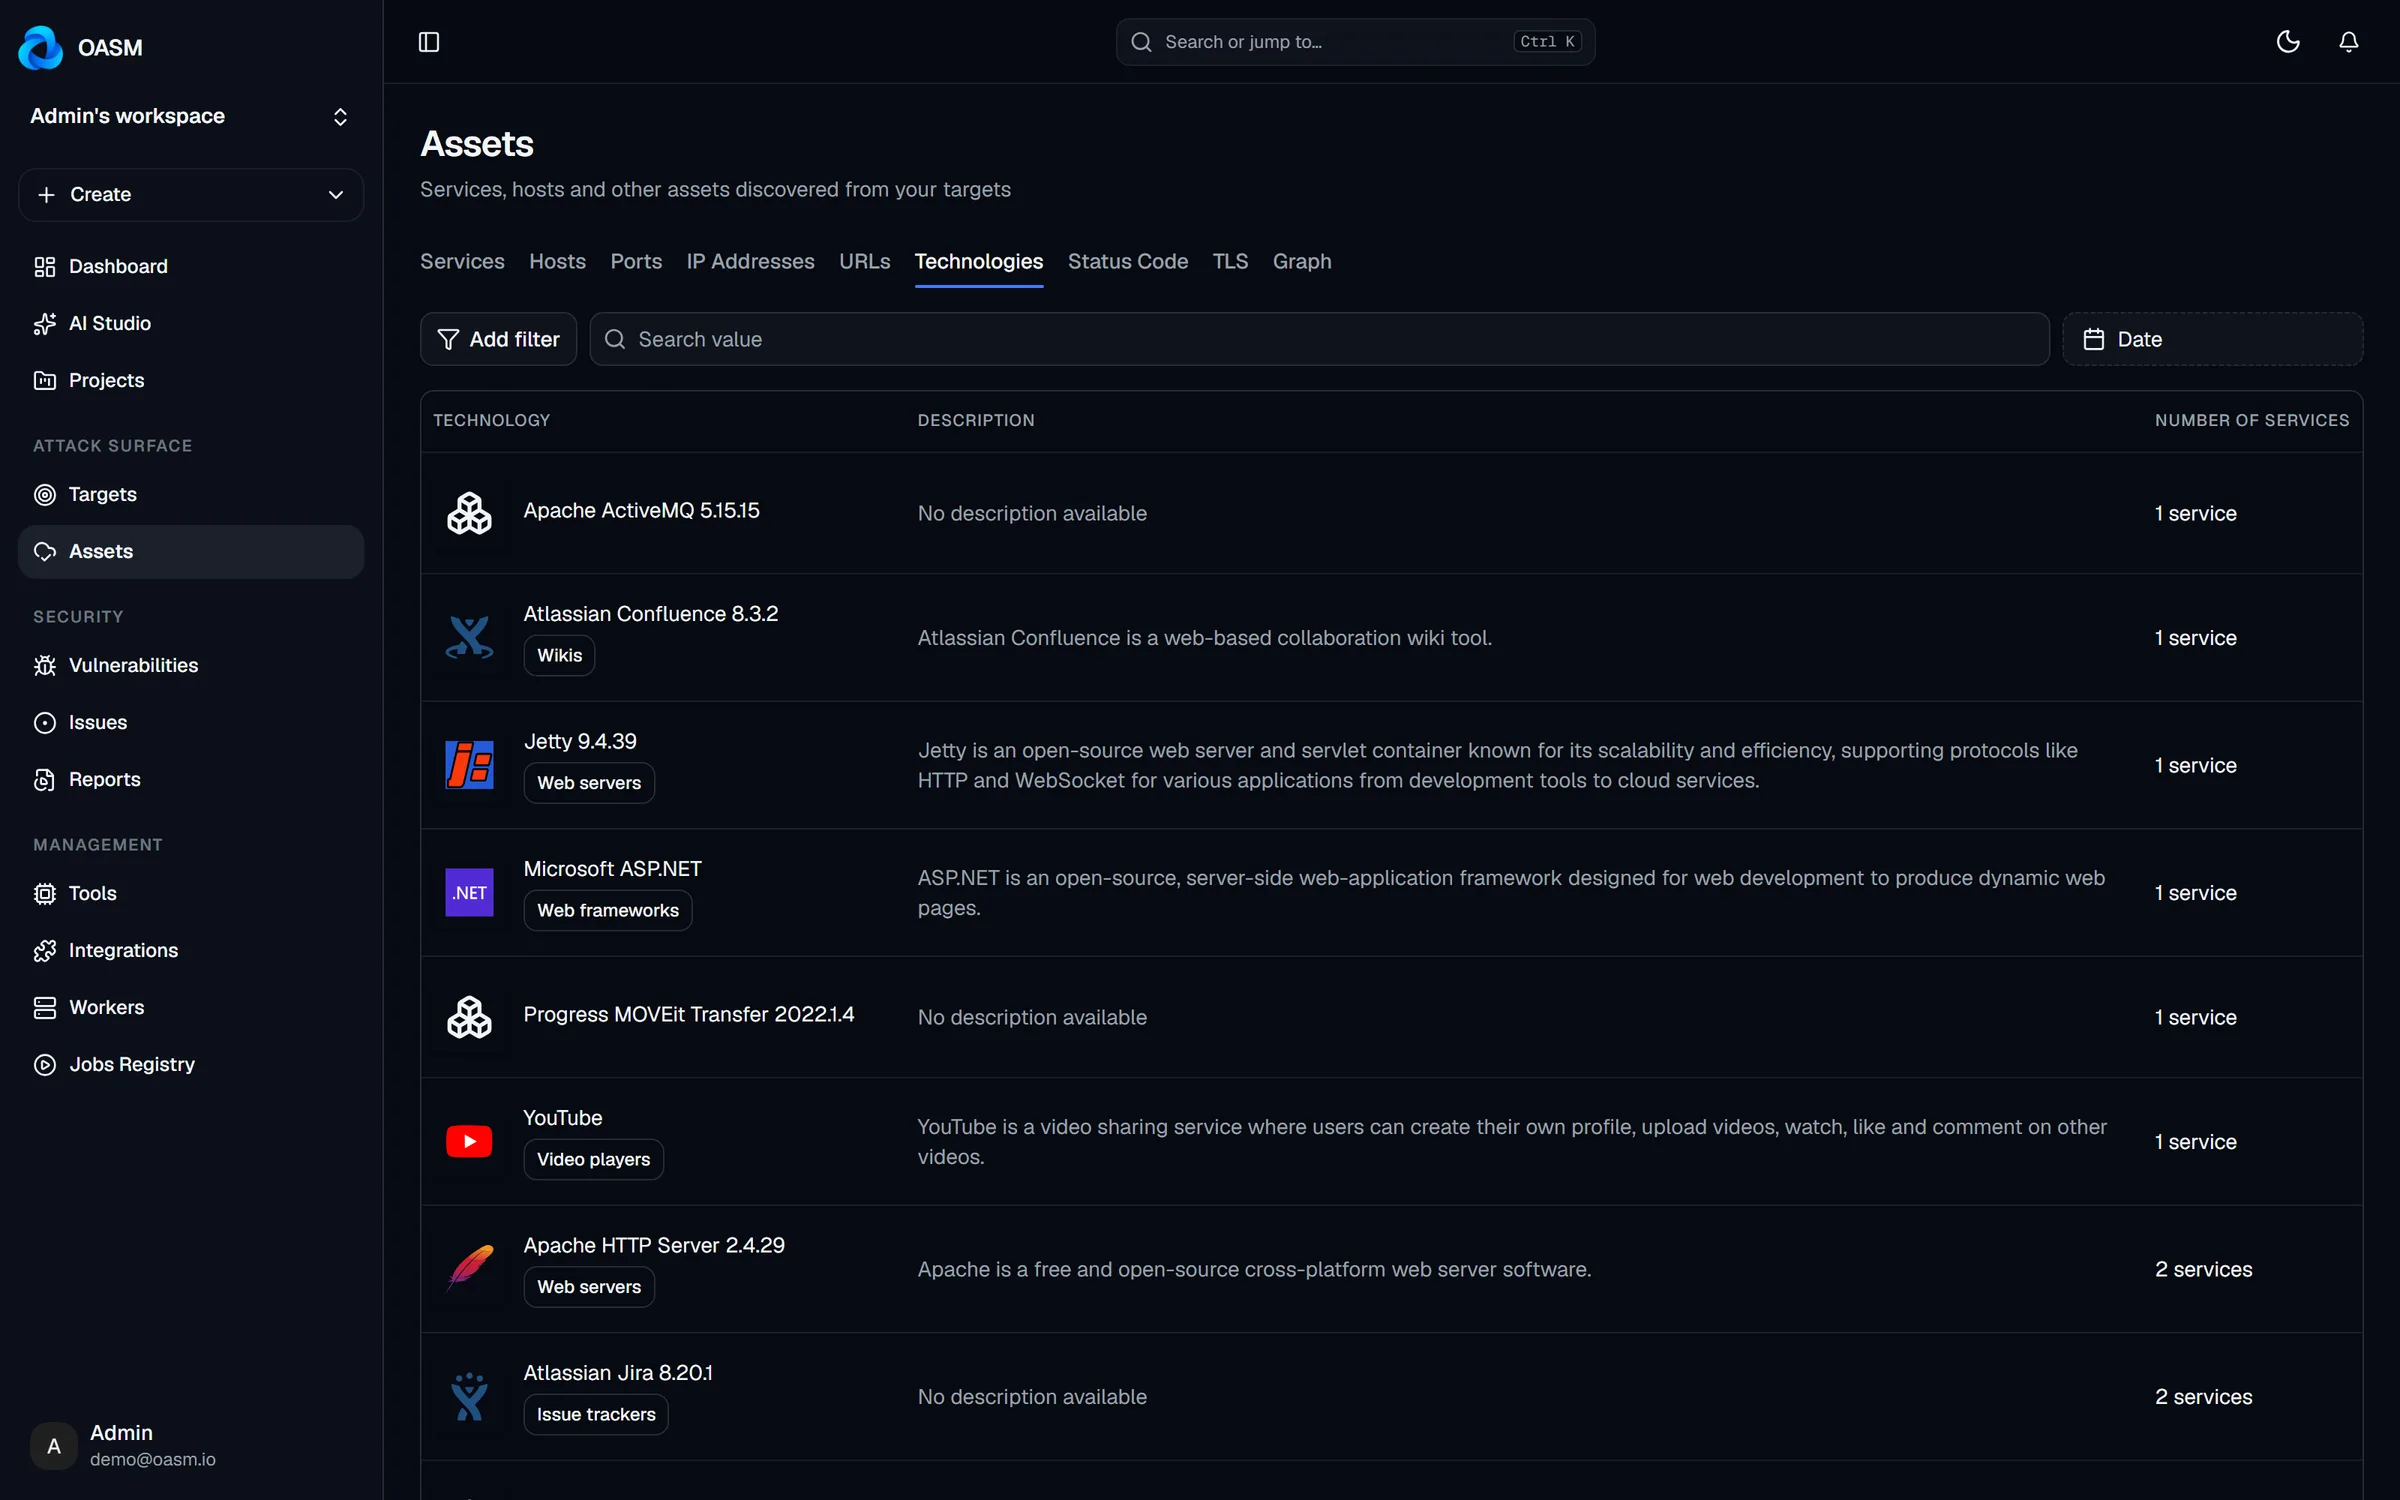
Passive sources turn one root into every host behind it.
Open ports, live services, titles and status codes.
AWS, Cloudflare, Vercel, GitHub and GitLab push assets in.
Know when a target has not been scanned for too long.
Track each target with its surface size, open findings by severity and last scan.
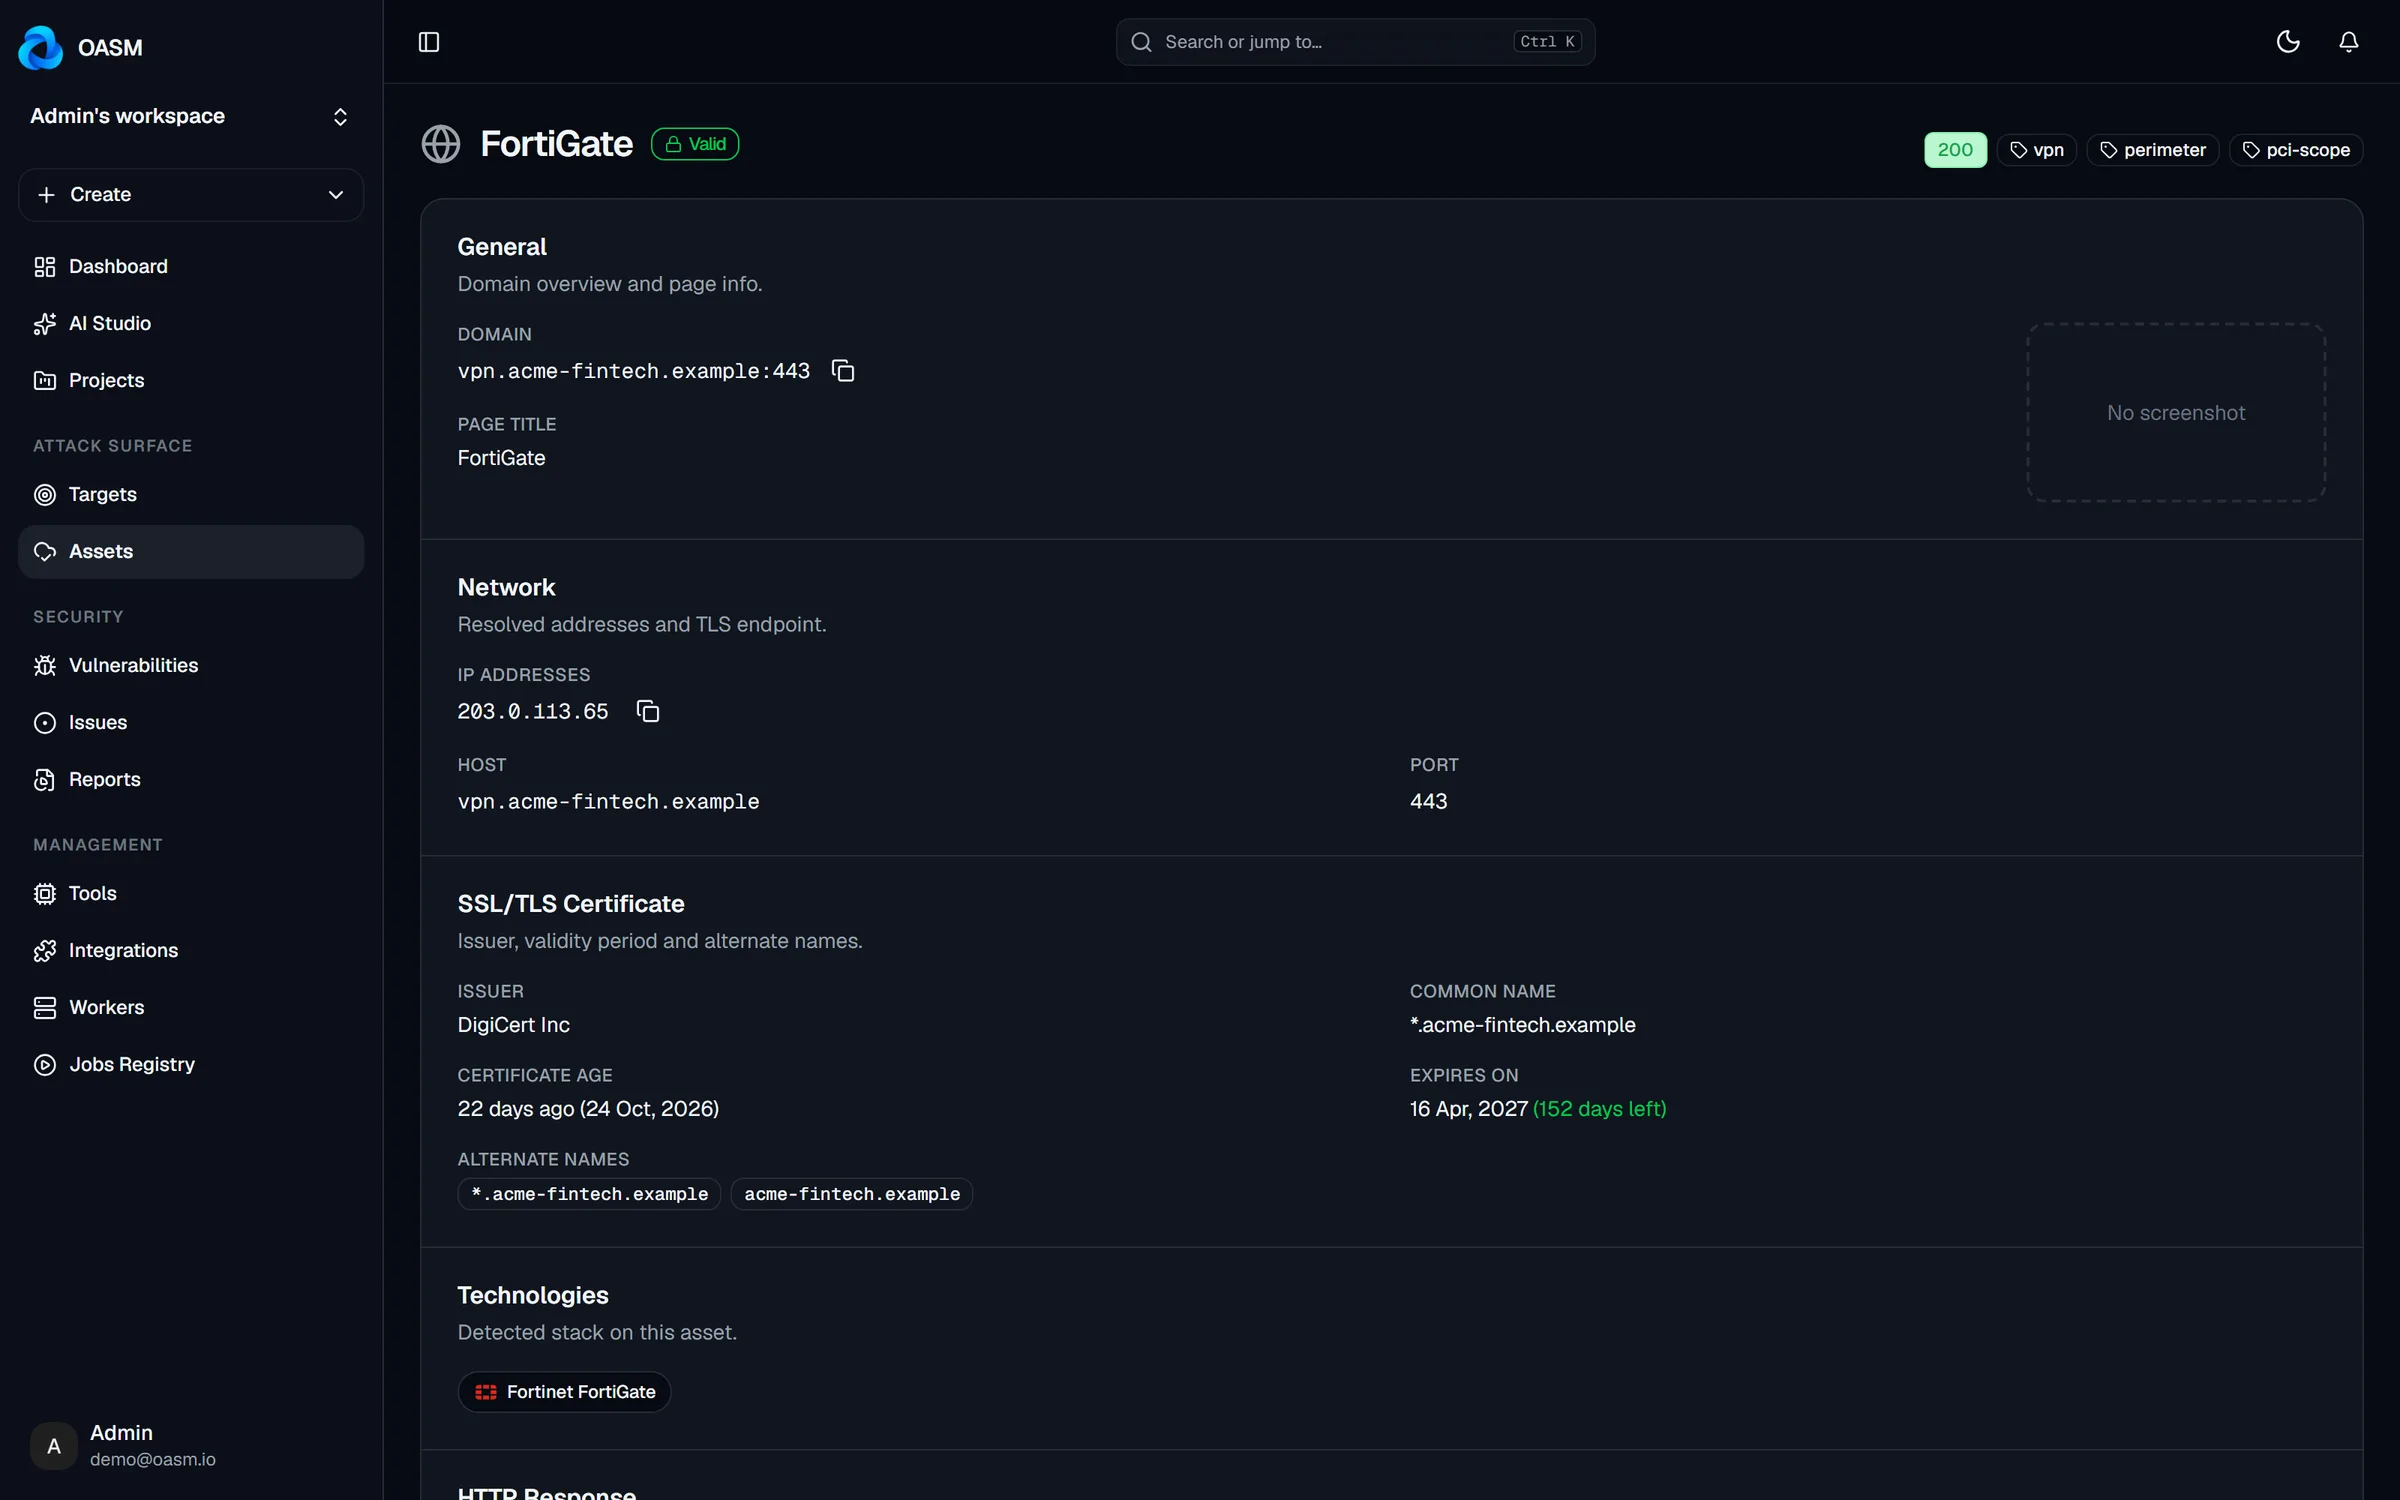
Response, certificate, technologies and findings for every service under a target.
Find shadow IT and forgotten hosts before they turn into an incident.
Seed a scope and get a full map of hosts and services to test.
Map an acquired company’s internet footprint from its domains.
Domains, single IP addresses, CIDR ranges and source-code repositories. Cloud integrations can also add assets automatically.
Free, open source and self-hosted. Your data never leaves your infrastructure.